
by Jordan Dean on Nov 16, 2026
A cyberattack doesn't have to steal a single password, empty a bank account, or demand a ransom to cause widespread damage. Sometimes, all it takes is changing the temperature of a refrigerator.
In October 2026, hackers remotely manipulated refrigeration systems at hundreds of supermarkets across France, causing food to spoil and businesses to suffer significant losses. Weeks later, attackers attempted to interfere with refrigeration systems protecting blood plasma at three French medical facilities. Meanwhile, the Pentagon was investigating whether freezer failures at several U.S. military bases could have involved malicious cyber activity.
Although these incidents have not been directly linked, they challenge the way most people understand cybercrime. We tend to associate hacking with stolen information, fraudulent emails, and financial extortion, yet attackers can also interfere with the physical systems that keep everyday life functioning.
And when those systems are responsible for preserving food, protecting medical supplies, or supporting military operations, the consequences can extend far beyond financial losses.
When a supermarket becomes the target of a cyberattack
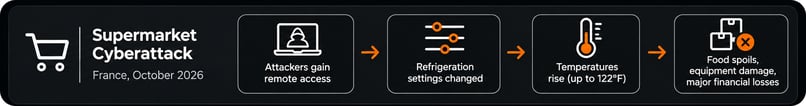
Most people walking into a grocery store don't think about cybersecurity. They expect the refrigerators to be cold, the food to be safe, and the shelves to be stocked. In October, those ordinary expectations were disrupted when hackers gained remote access to refrigeration management systems used by hundreds of French supermarkets, including locations operated by Carrefour and Intermarché.
According to CNN, attackers manipulated refrigeration settings, driving temperatures in some units as high as 50 degrees Celsius, or 122 degrees Fahrenheit. Equipment designed to preserve food was effectively turned into a source of heat, leaving large quantities of fresh and frozen products unsafe for consumption. Reports also emerged of fires associated with affected equipment.
The CEO of Intermarché estimated that the nationwide cost of damages could reach “tens of millions of euros in a single day”, illustrating how interference with a seemingly ordinary piece of equipment can produce enormous consequences.
The attack exploited weaknesses in internet-connected refrigeration management technology, which allows retailers and maintenance providers to monitor and adjust equipment remotely. While these capabilities make operations more efficient, they also create opportunities for unauthorized access when systems are inadequately secured. The software manufacturer, Danfoss, indicated that affected systems had not received a previously recommended firmware update.
What makes this incident particularly interesting is how little it resembles the cybercrime most people recognize. The attackers didn't need to steal customer information or compromise financial accounts to create widespread disruption. By manipulating a function that consumers rarely think about, they were able to interfere with physical operations and cause losses that couldn't simply be reversed by restoring a computer system. On the list of cybersecurity priorities, fridges don’t often make the cut.
The identities and motives of those responsible remain unclear, but the incident demonstrated how vulnerable essential services can become when the technology controlling them is accessible through digital networks.
And while spoiled groceries can represent devastating financial losses, the implications become considerably more serious when similar technology is responsible for preserving medical supplies.
From spoiled groceries to threatened blood plasma
In early November, another refrigeration-related cyberattack emerged in France, this time involving facilities operated by the Établissement français du sang (EFS), the country's national blood service.
Between November 1 and 2, 2026, attackers reportedly gained access through a third-party refrigeration service provider and attempted to manipulate temperature and defrost settings at three facilities storing blood plasma and other biological materials.
Unlike spoiled groceries, which can generally be replaced through commercial supply chains, blood plasma is a critical medical resource that depends on carefully controlled storage conditions. Temperature fluctuations can compromise its suitability for medical use, potentially forcing healthcare providers to discard supplies that require significant time and resources to collect and process.
Fortunately, monitoring systems identified abnormal activity before the stored plasma was damaged, allowing personnel to secure the equipment and move supplies as a precaution.
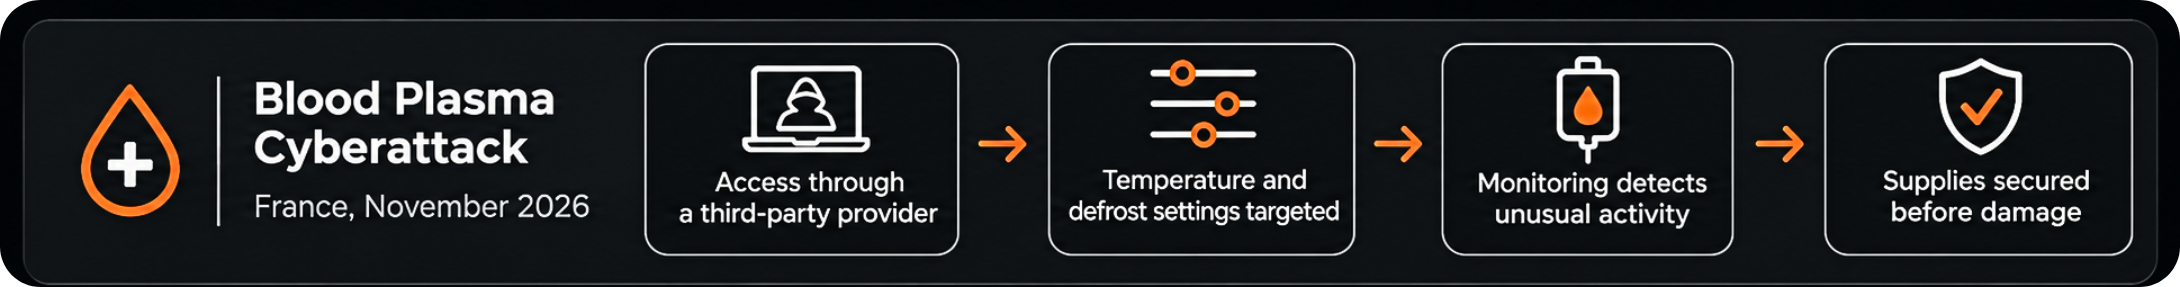
According to eSecurity Planet, the attackers reportedly accessed the refrigeration equipment through a compromised supplier rather than directly breaching the medical facilities themselves. This detail is especially concerning because organizations can invest heavily in protecting their own networks while remaining exposed through outside companies responsible for maintaining essential equipment.
Although the attacks on French supermarkets and medical facilities have not been conclusively linked, they demonstrate how compromised access to refrigeration controls can threaten vastly different operations. In one case, businesses suffered substantial losses. In the other, monitoring and intervention prevented a potentially serious disruption to medical supplies.
The concern becomes even broader when similar equipment failures begin raising questions within the military.
The Pentagon is investigating a similar concern
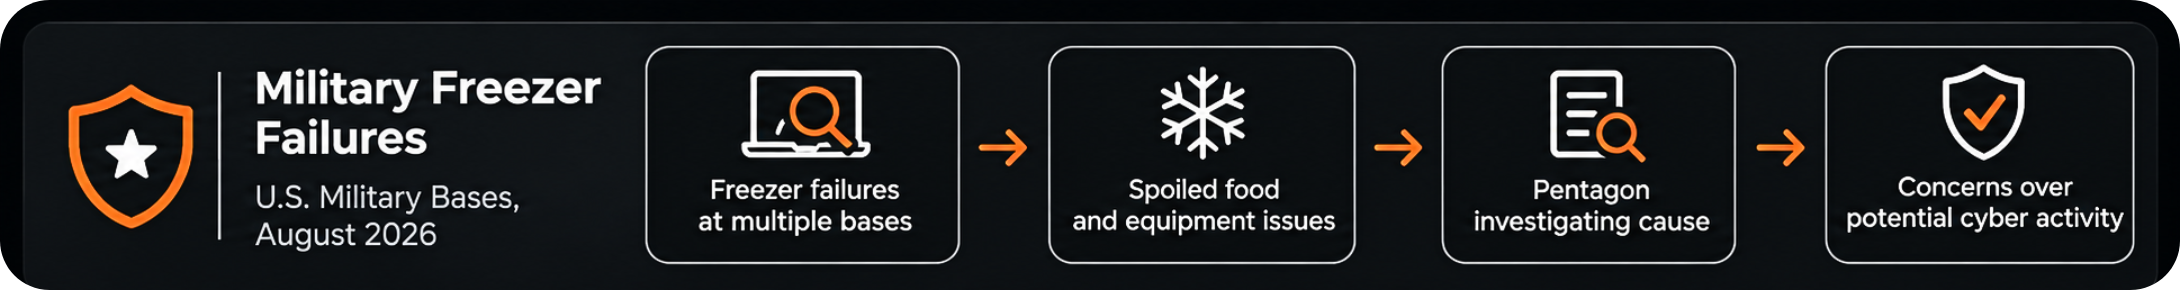
In the United States, the Pentagon is investigating refrigeration failures reported at commissaries on at least six military bases during August 2026. The incidents resulted in spoiled food and prompted questions about whether malicious cyber activity could have contributed to the failures.
As reported by eSecurity Planet, investigators have not confirmed that the failures were caused by a cyberattack, and there is no established connection between the military incidents and the attacks in France.
Nevertheless, the investigation highlights an often-overlooked aspect of cybersecurity. Military readiness depends on far more than protecting classified information, weapons systems, and communications networks. It also relies on the infrastructure supporting personnel and everyday operations, including food storage, utilities, transportation, and logistics.
A refrigeration failure may sound insignificant compared with an attack on a military network, but disruptions to supporting infrastructure can create logistical challenges, financial losses, and additional demands on personnel. An adversary seeking to interfere with operations doesn't necessarily need access to an organization's most sensitive systems if less obvious vulnerabilities can cause meaningful disruption.
Whether the military failures ultimately prove to be cyber-related remains an open question. Their investigation reinforces the importance of considering security risks beyond traditional computers and networks.
Cybercrime isn't always about the money
For years, the public conversation surrounding cybercrime has focused heavily on financial gain. Criminals steal credit card numbers, compromise bank accounts, demand ransomware payments, or sell sensitive information. While these threats remain widespread, they represent only part of what malicious cyber activity can accomplish.
Some attackers are motivated by ideology, geopolitical objectives, retaliation, or the desire to undermine an institution. Others may be interested in demonstrating their capabilities or disrupting operations simply because they can. In certain circumstances, the disruption itself can be the objective, particularly when attackers seek to create uncertainty or undermine public confidence.
Consider the consequences of a coordinated attack on supermarket refrigeration systems. Even without a ransom demand, businesses must dispose of spoiled products, restore equipment, and reassure customers that their food is safe. Suppliers may face unexpected demand, while consumers may begin questioning the reliability of products they purchase.
Now apply that same principle to hospitals, water treatment facilities, or electricity providers. The stakes become considerably higher because the public depends on these services for basic needs, and disruptions can affect health, safety, and access to essential resources.
Although the motives behind the recent refrigeration attacks remain unclear, these incidents demonstrate why financial theft alone is an incomplete measure of cyber risk. An attack can cause severe damage even when no money is stolen, particularly when it interferes with systems people depend on.
The overlooked systems connecting cybersecurity to the physical world
The common thread running through these incidents is Operational Technology, often called OT. Unlike traditional information technology, which primarily processes and stores data, Operational Technology monitors and controls physical processes, including refrigeration, manufacturing equipment, industrial machinery, and critical infrastructure.
Historically, many of these systems operated in relatively isolated environments. Today, remote monitoring, connected sensors, and third-party maintenance services have made them increasingly accessible through digital networks. These advancements improve efficiency, but they also create new opportunities for attackers when remote access is inadequately secured.
The refrigeration incidents illustrate how a manipulated setting can alter the physical environment, while a compromised vendor account may provide access to equipment across multiple facilities. Unlike many traditional data breaches, the consequences cannot always be reversed by resetting credentials or restoring a backup. Spoiled food cannot be recovered, and compromised medical supplies may need to be discarded.
For organizations operating critical equipment, cybersecurity must extend beyond protecting databases and employee devices. It requires visibility into connected systems, controlled third-party access, timely security updates, and monitoring capable of identifying unusual equipment behavior before it causes physical damage.
The French blood plasma incident demonstrated the value of these protections. Although attackers reportedly gained access to refrigeration controls, monitoring and response procedures prevented the attempted manipulation from destroying medical supplies.
The next cyberattack may not look like a cyberattack
A supermarket refrigerator, a medical plasma freezer, and a military commissary might initially seem to have little in common. Yet all three depend on equipment whose failure can affect far more than the organization operating it, whether through financial losses, threats to essential supplies, or disruptions to critical operations.
The recent incidents do not establish a coordinated campaign, and the military failures remain under investigation. What they reveal is a shared concern about society's growing dependence on connected technology and the potential consequences when that technology becomes vulnerable to malicious interference.
The implications extend well beyond refrigeration. Manufacturing facilities, transportation networks, healthcare equipment, utilities, and countless other essential services rely on digital systems to control physical processes. As these environments become more connected, organizations must recognize that the consequences of a cyberattack may increasingly be felt far beyond a computer screen.
The next major cyberattack may not require anyone to click a malicious link or surrender their credentials. It may begin with an unauthorized change to a system most people never knew was connected to the internet, and end with consequences that reach into the physical world.
As cyberthreats increasingly extend beyond traditional networks, organizations need to understand where they're exposed and how quickly they can respond. RADICL helps organizations strengthen their cybersecurity posture through continuous threat monitoring, advanced detection, and expert-led response, helping identify threats before they escalate into costly disruptions.
What Is Password Spraying? Low-and-Slow Account Compromise
Credential Stuffing: Bulk Account Takeover Explained

No Comments Yet
Let us know what you think