Build a solid NIST CSF foundation that secures your environment

RADICL's Managed Compliance Adherence expertly guides, builds, and operates your NIST CSF 2.0 program end to end by pairing certified experts and an AI-powered platform with the hard-to-do security that CSF requires.
Talk to a Specialist See how it works

NIST CSF is the standard that mature organizations use to prove structured, disciplined security. RADICL operationalizes it so your environment actually runs to the framework, not just claims to.

The framework that proves you truly manage risk

Small and mid-sized organizations now face the same ransomware gangs and nation-state actors as large enterprises and your customers, insurers, boards, and regulators increasingly expect proof of enterprise-grade security. NIST CSF 2.0 is that proof.

Rooted in security

Rooted in security,
expert in compliance

RADICL was founded to deliver enterprise-grade threat protection and expert-guided compliance. With us, you get a partner that does the heavy lifting, not just another tool to run yourself.
Operating model

An operating model,
instead of a one-time audit

CSF done right is a continuous process. We identify posture gaps, guide foundational controls, and maintain alignment over time to provide the attention most teams can't give while still running the business.
Board

Board and stakeholder
confidence

RADICL delivers operationalized best practices and real-time posture visibility that give leadership, boards, insurers, and auditors confidence that your organization is secure.

We guide, build, and operate your CSF foundation

Managed Compliance Adherence (MCA) does the heavy lifting of NIST CSF 2.0 for you across all 106 subcategories, six functions, and 23 categories — combining certified experts, an AI-powered platform, and the security operations that the framework demands.

GUIDE

Expert-guided
assessment

We onboard your team (and MSP, if you have one) to the platform, then guide a comprehensive assessment across all 106 CSF subcategories to clarify exactly where you stand and where to focus. We optimize scope so effort goes where risk actually is, instead of gold-plating everything.

BUILD

Guided remediation
& evidence

RADICL guides (and automates, where possible) remediation of gaps against CSF best practices. Jett, our AI agent, clarifies hard-to-define requirements and drafts documentation. Notes, screenshots, and files are captured automatically, so the foundation you build is always audit-ready.

OPERATE

Ongoing operation
& hard-to-do security

CSF isn't finished on the go-live date. We operate the hardest, costliest outcomes for you (such as 24/7 detection and response, vulnerability management, awareness training, and log analytics) while real-time dashboards keep leadership current and alignment intact as threats evolve.

Div Line_Desktop
Div Line_Mobile

From uncertainty to operationalized best practices

Our proven process turns the CSF framework into a program your organization really runs — and keeps running.

The hard-to-do security that CSF requires, off your plate

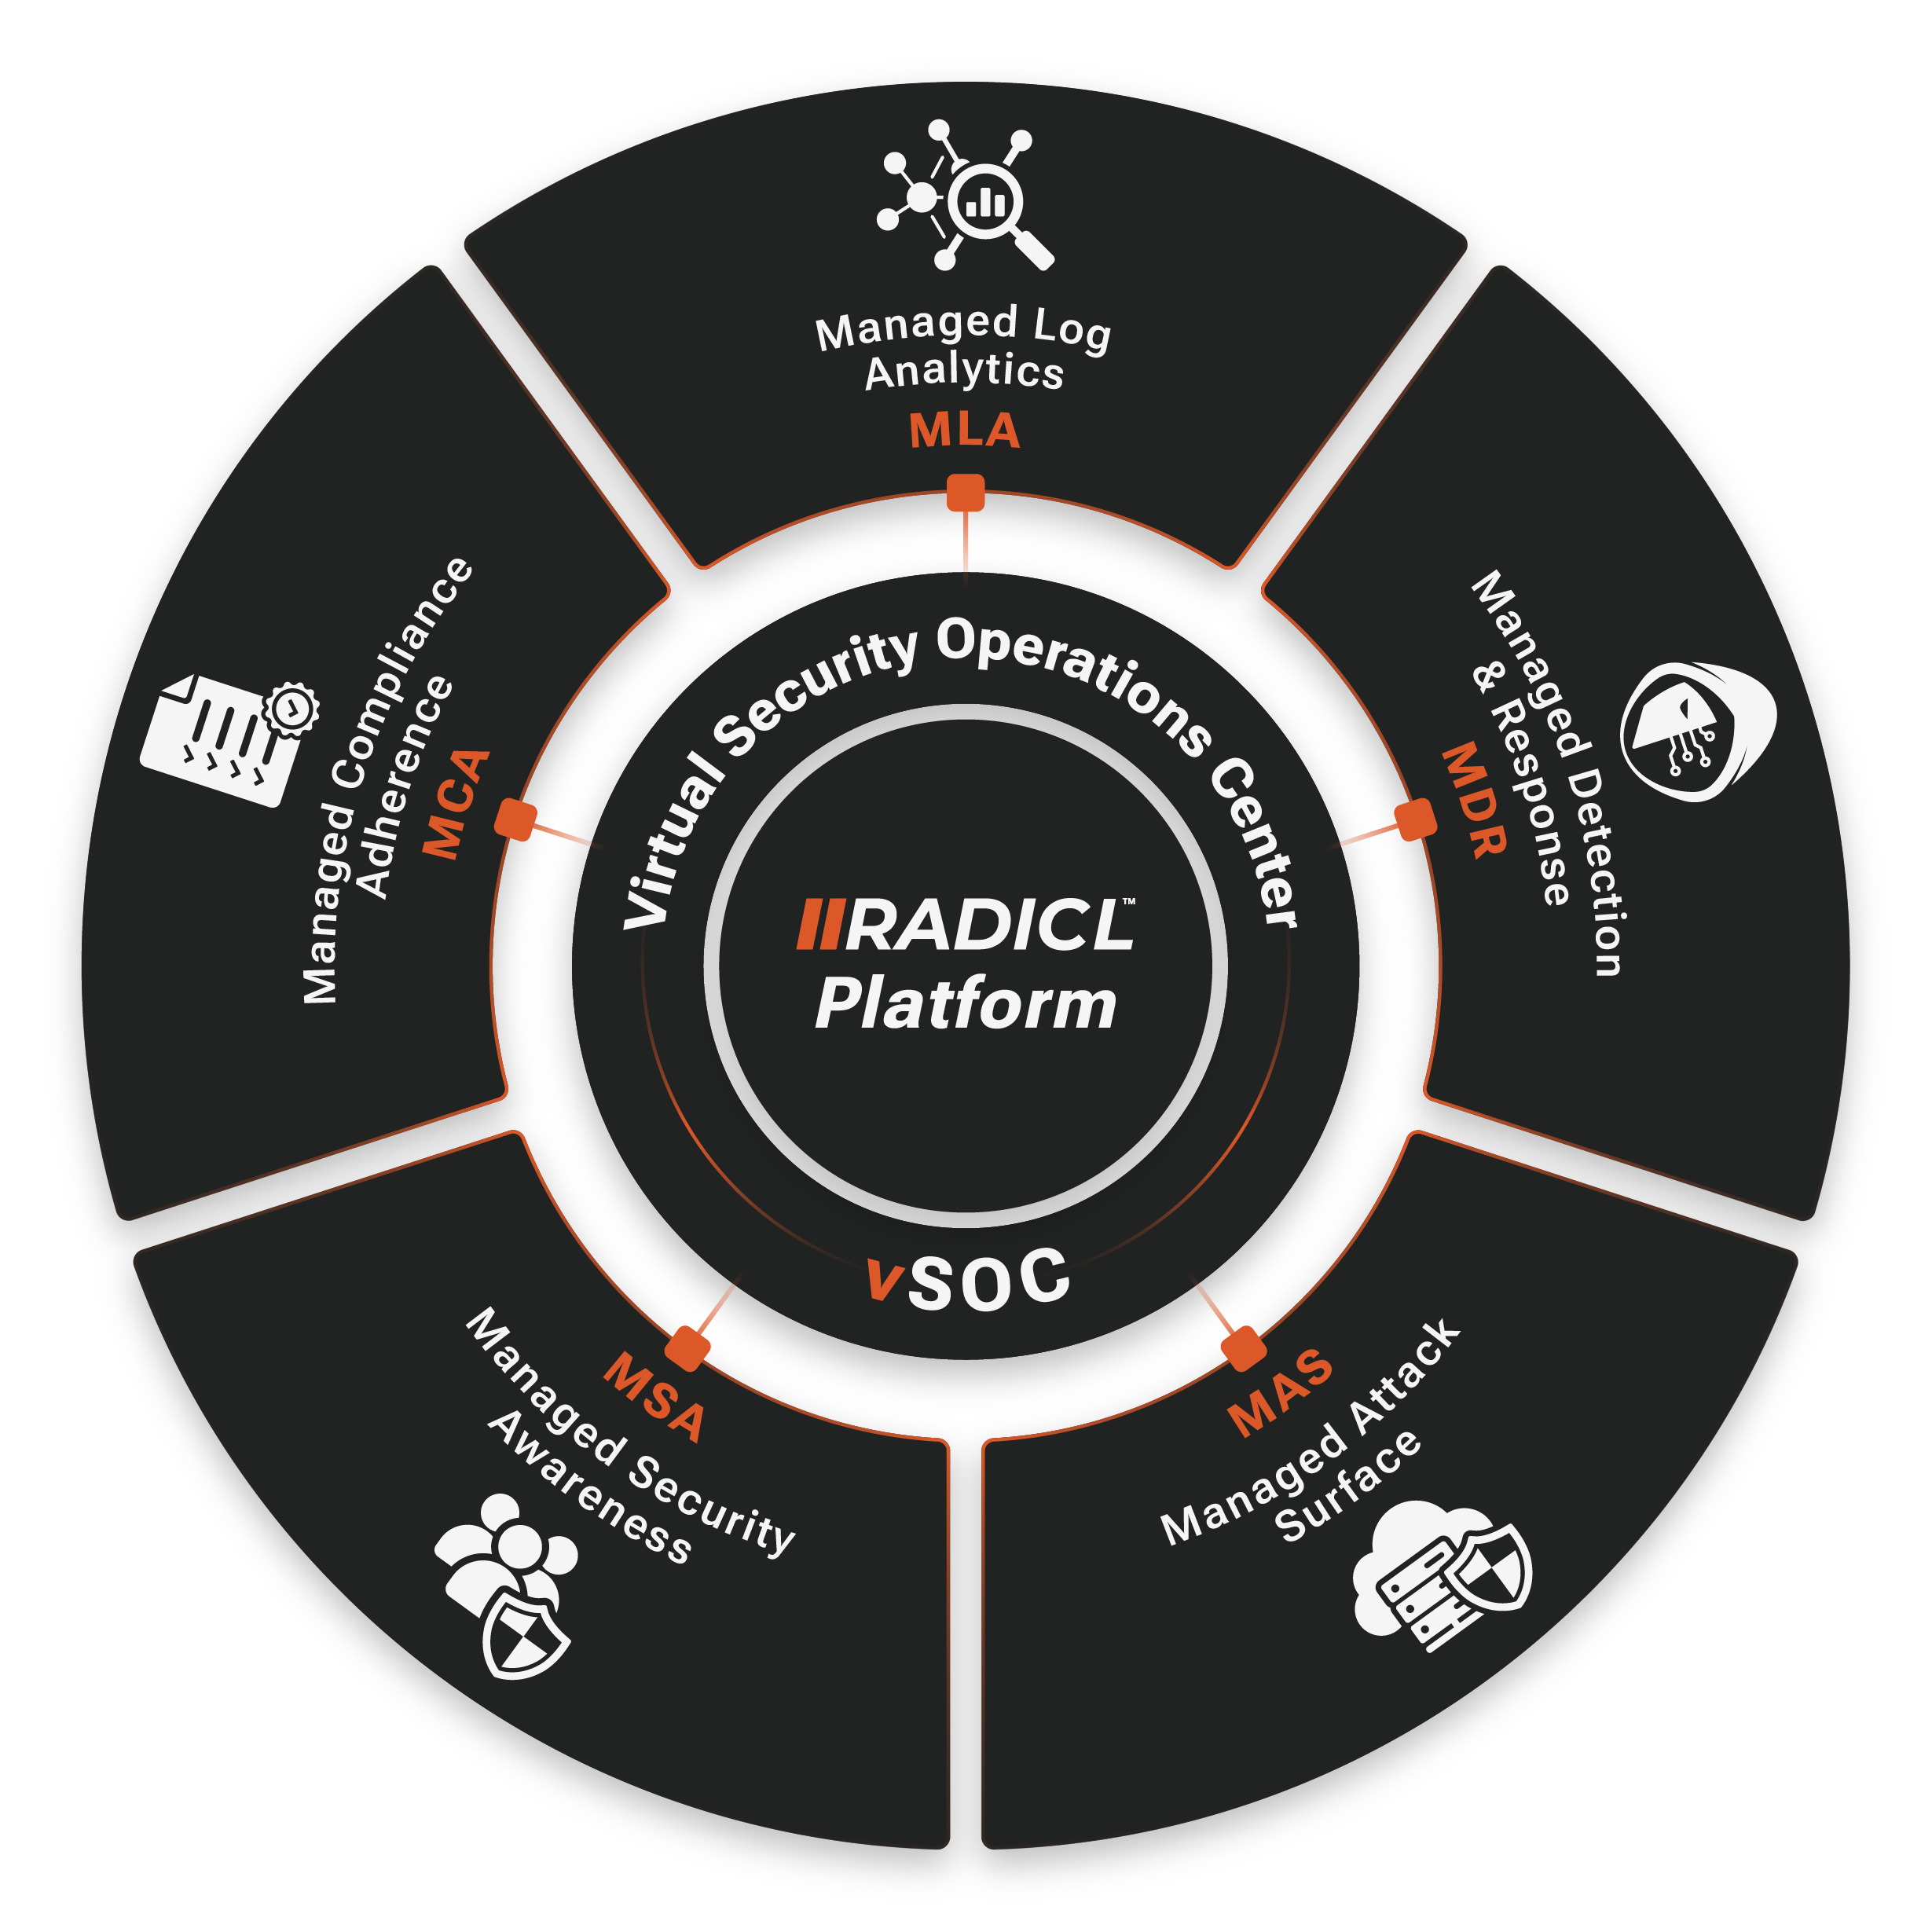
Many CSF outcomes are the hardest and costliest to realize because they mean procuring, integrating, and running dedicated security technology and expert teams. RADICL's Cybersecurity-as-a-Service Platform operates these for you by directly addressing up to 106 CSF controls in the areas that most reduce incident risk.

MDR

Managed Detection & Response

A dedicated Security Operations Center detects successful attacks across endpoint, identity, network, and cloud, with proactive threat hunting for evasive threats. Specialized responders contain and mitigate incidents using pre-built playbooks to minimize downtime, cost, and brand damage.

Maps to: Continuous Monitoring (DE.CM) · Adverse Event Analysis (DE.AE) · Incident Management, Analysis & Mitigation (RS.MA/AN/MI) · Recovery execution (RC.RP) · managed EDR endpoint protection (PR.PS)

MLA

Managed Log Analytics

Log data is the foundation of traceability and accountability. RADICL centralizes collection and analysis with SIEM-like analytics that feed real-time threat detection and keep logs searchable and retained for forensic analysis whenever an incident occurs.

Maps to: Continuous Monitoring & log analysis (DE.CM/AE) · Incident forensics (RS.AN) · audit-log evidence and retention supporting oversight (GV/ID)

MAS

Managed Attack Surface

Automated scanning continuously assesses your environment, with risk-based prioritization and expert-guided remediation that proactively shrinks the attack surface and hardens your defenses over time.

Maps to: Risk Assessment & vulnerability identification (ID.RA) · asset visibility (ID.AM) · hardening & platform security (PR.PS)


MSA

Managed Security Awareness

Human error remains a leading risk factor. Tailored training with interactive elements like simulated phishing reinforces good behavior, while participation and performance tracking demonstrate the awareness outcomes CSF expects.

Maps to: Awareness & Training (PR.AT)


From reactive tools to proactive protection

See how organizations replace piecemeal tools with RADICL's comprehensive Platform to gain a NIST CSF foundation, 24/7 threat hunting, and the evidence to prove their security posture to anyone who asks.

Read case study

What a strong NIST CSF
posture protects

Reduced incident risk

Reduced incident risk

Operationalizing the outcomes that matter most (monitoring, response, and vulnerability management) lowers cyber incident odds.
Provable to stakeholders

Provable to stakeholders

Evidence capture and real-time posture give customers, insurers, boards, and auditors proof that security is being done the right way.
Continuous

Continuous, not one-time

Ongoing assessment and operation keep you aligned as threats and the business change without a scramble when the next review arrives.
A foundation for what's next

A foundation for what's next

A running CSF program is the base that maps cleanly toward CMMC, 800-171, PCI DSS, HIPAA, GLBA, and other obligations as they arise.
The RADICL advantage

Enterprise-grade discipline, without hiring a security team.

Number-1
Expert-guided assessment across all 106 CSF subcategories
Number-2
Guided, often automated remediation for identified gaps
Number-3
Hard-to-do security operated for you across MDR, MAS, MSA, and MLA
Number-4
Evidence capture and real-time posture, always audit-ready
Number-5
Security and compliance integrated in one CSaaS platform
Div Line_Desktop
Div Line_Mobile

Why customers choose RADICL

One platform.
Experts, AI, and 24/7 operations.

Security and compliance, integrated. RADICL operates the toughest CSF outcomes while your team keeps running the business, giving you full transparency into everything we do on your behalf.

RADICL Platform

Ready to build a NIST CSF foundation that runs itself?

Schedule a Demo Call (720) 738-7529

Frequently Asked Questions

What is the NIST Cybersecurity Framework (CSF)?

NIST CSF is a voluntary framework for managing and reducing cybersecurity risk. CSF 2.0 defines six core functions — Govern, Identify, Protect, Detect, Respond, and Recover — spanning 23 categories and 106 subcategories that describe desired security outcomes like asset management, vulnerability management, incident response, awareness training, and continuous monitoring. It's the standard mature organizations use to demonstrate structured, disciplined security. RADICL operationalizes CSF so your environment actually runs to the framework, not just claims to.

Who should adopt NIST CSF?

Any organization that wants to manage cyber risk with rigor and prove it. Small and mid-sized organizations increasingly face the same threats as large enterprises, and customers, insurers, boards, and regulators increasingly expect evidence of enterprise-grade practices. Because CSF is risk-based and flexible, it fits organizations at any maturity level — and maps cleanly toward other obligations like CMMC, NIST 800-171, PCI DSS, HIPAA, and GLBA as they arise.

How does RADICL's MCA help with NIST CSF?

Managed Compliance Adherence does the heavy lift end to end. We onboard your team to the platform, guide a full assessment across all 106 subcategories, guide (and where possible automate) remediation, and capture evidence automatically. Our AI agent, Jett, clarifies hard-to-define requirements and drafts documentation, and real-time dashboards keep leadership informed. You get certified expertise plus automation — not just a software tool.

What is the "hard-to-do" security CSF requires, and how do you operate it?

Some CSF outcomes are the hardest and costliest to realize because they require dedicated technology and expert teams running around the clock. RADICL operates these for you: Managed Detection & Response (Detect/Respond/Recover), Managed Log Analytics (Detect/Respond), Managed Attack Surface (Identify/Protect), and Managed Security Awareness (Protect). Together they directly address up to 106 CSF controls in the areas that most reduce incident risk.

Does RADICL replace our IT team or MSP?

No. Your IT team or MSP handles infrastructure and day-to-day operations. RADICL overlays managed security and compliance operations on top — the specialized work most IT providers aren't staffed to cover — and your team and MSP are onboarded to the platform to collaborate with full transparency into everything we do.

How is NIST CSF different from NIST 800-171 and CMMC?

NIST 800-171 and CMMC are requirements for defense contractors handling Controlled Unclassified Information. NIST CSF is a broader, voluntary, risk-based framework any organization can adopt to structure and prove its security program. RADICL supports all of them on one platform, and a running CSF foundation makes those other frameworks far easier to reach.