Cybersecurity for Credit Unions

Strong cybersecurity, simplified. RADICL delivers comprehensive 24/7 protection and drives NCUA-ready compliance for credit unions — safeguarding member data and community trust without the expense and complexity of building your own security team.
Talk to a Specialist Learn About Our Platform
  • ACS

  • Aerial Machine & Tool

  • Agile Space Industries

  • Anew Solutions

  • Barn Owl Tech

  • Blue Sky Innovators

  • C Speed

  • DLZ

  • Electra Aereo

  • Firehawk Aerospace

  • G&H

  • Havoc AI

  • HTX Labs

  • Miltope

  • MAK Technologies

  • Red6

  • SpektreWorks

  • Stonhard: Commercial & Industrial Flooring

  • Trenton Systems

  • Urban Sky

  • VATN Systems

  • Zone5 Technologies

Credit unions are the financial foundation of their communities

Millions of families, small businesses, teachers, and first responders trust their credit union to keep their money safe. That trust is exactly what attackers target. RADICL was founded to protect what matters most — and we bring the same seriousness to defending a community's finances that we bring to protecting national security.

“If you cannot afford robust security, you have no business being in business. We need peace of mind — the kind we can confidently show our board and our examiners. That is exactly what RADICL delivers for us.”


Nicole Smith | President & CEO
at U S Federal Credit Union

“If you cannot afford robust security, you have no business being in business. We need peace of mind — the kind we can confidently show our board and our examiners. That is exactly what RADICL delivers for us.”


Nicole Smith | President & CEO at U S Federal Credit Union

Why credit unions
get targeted

Ransomware syndicates and fraud rings pursue credit unions because member accounts, personal data, and payment systems availability convert to money. A single incident can freeze member access, trigger NCUA scrutiny, and erode the community trust a credit union is built on.

These factors make Credit Unions a rich target for cybercriminals.

Icon5
Member funds & data
Account details, SSNs, and payment access convert straight to fraud and theft.
Icon-64
Member trust
A breach erodes the community relationships that make a credit union what it is.
Icon-100
NCUA scrutiny
Part 748, the 72-hour rule, and ISE exams put your program under real examination.
Uptime matters
Uptime matters
Members expect 24/7 access. An outage is a community event, not an IT ticket.
Lean teams + tool sprawl
Attackers bet a one- or two-person IT team will detect late and respond slowly.

Top pain points for
credit unions

MSP ≠ cybersecurity

Many credit unions believe their MSP has security covered. Most MSPs aren't staffed to deliver an expert-driven 24/7 security operations center (SOC).

NCUA proof burden

Protecting member data is only half the job. Examiners want a written program mapped to a framework, with evidence you can produce on demand.

The 72-hour clock

You must notify NCUA within 72 hours of a reportable incident — including one that starts with a third-party vendor. That requires real detection and forensics.

Vendor sprawl & cost

A SIEM here, an EDR there, a training tool, a scanner — pieced together across platforms, driving up cost, complexity, and the gaps between them.

Alert & vulnerability overload

Too much noise for a small team means slow triage, delayed patching, and recurring exam findings.

No security team to hire

A 24/7 SOC and a compliance program are out of reach to staff internally at credit union scale — but the risk is enterprise-grade.

Div Line_Desktop
Div Line_Mobile

How RADICL Does Threat Detection & Response

We turn security into a running operation for your credit union: ingest the right signals, qualify what matters, investigate what's real, then coordinate response and track every fix to verified closure — so you can prove outcomes for the NCUA and protect members every hour of every day.

See how RADICL MDR works
1
Signals In
Ingest endpoint, identity, and network telemetry across your environment.
2
Analyze
Apply analytics to qualify activity and catch compromise before it becomes noise.
3
Triage
Our autonomous vSOC filters the noise and confirms what's real.
4
Investigate
Determine impact and next steps, documenting findings clearly.
5
Respond
We lead response and assign precise remediation to your IT team or MSP.
6
Track to Closure
Confirm progress and document outcomes so issues don't linger.
7
Improve Resiliency
Harden what matters most so the same issue doesn't repeat.

The hardest cybersecurity controls for credit unions

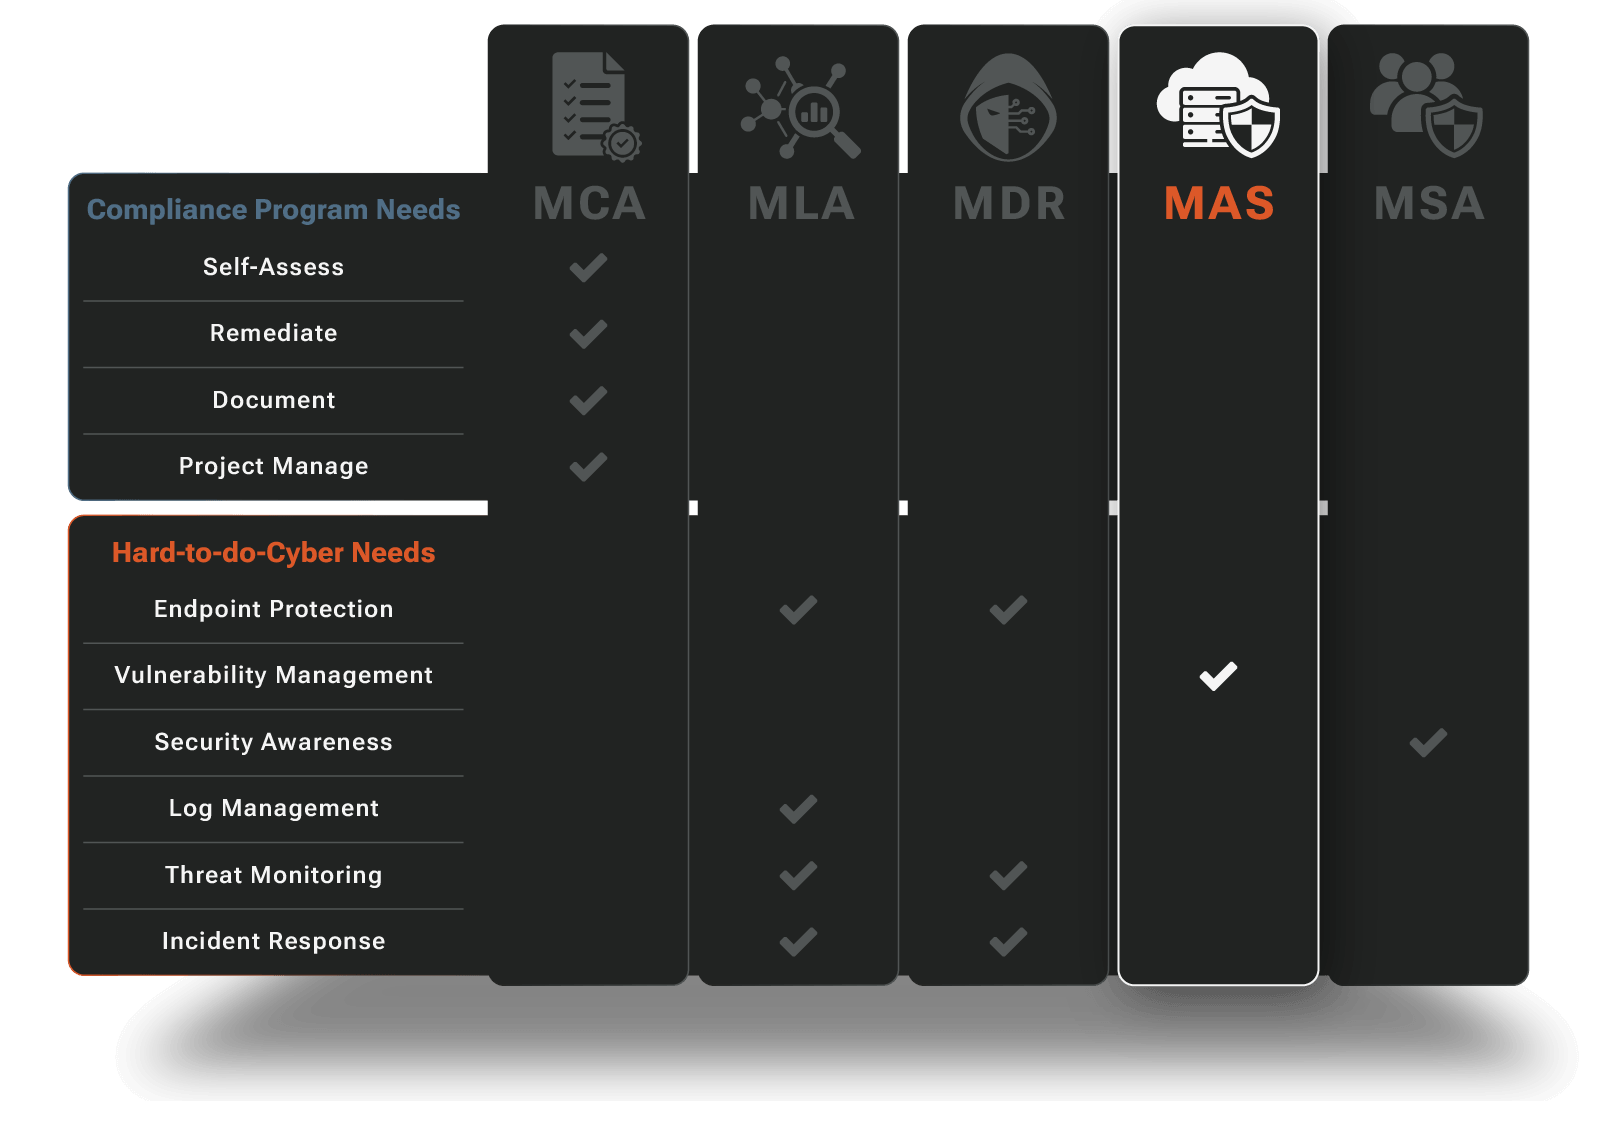
NCUA expectations and NIST CSF converge on the same operational controls — the ones hardest to implement and sustain without dedicated security staff. These capabilities most reduce cyber incident risk, and RADICL is built to operate them continuously, not as a one-time project.

Log Management

Log Management

Collect, retain, and make logs searchable for investigation and NCUA exam evidence — with a one-year archive.
Incident Response

Incident Response

24/7 coverage, coordinated execution, and documented outcomes — ready for the 72-hour notification clock.
Vulnerability Management

Vulnerability Management

Prioritize what matters, drive remediation at a manageable pace, and verify closure.
Security Awareness

Security Awareness

Reduce human-driven risk with measurable training and phishing simulations informed by real threats.

One trusted partner. One platform.
Complete protection.

What credit unions want is strong cybersecurity, simplified — not a stack of tools bought from different vendors and stitched together, each adding cost, complexity, and gaps. RADICL drives your NCUA compliance and verification program and handles the security operations most teams can't staff — the work that most reduces incident risk — all delivered by one team through one platform, with full transparency into everything we do.

Pieced together

  • Separate SIEM, EDR, scanner, training vendors
  • Multiple contracts, portals, and invoices
  • Gaps between tools no one owns
  • Compliance is your problem to assemble
  • You integrate, monitor, and chase fixes

RADICL CSaaS

  • Detection, response, logs, vuln mgmt & training in one
  • One partner, one platform, one relationship
  • End-to-end ownership, nothing falls through
  • We drive your NCUA / NIST CSF program
  • 24/7 vSOC operates it with you, transparently

See the difference

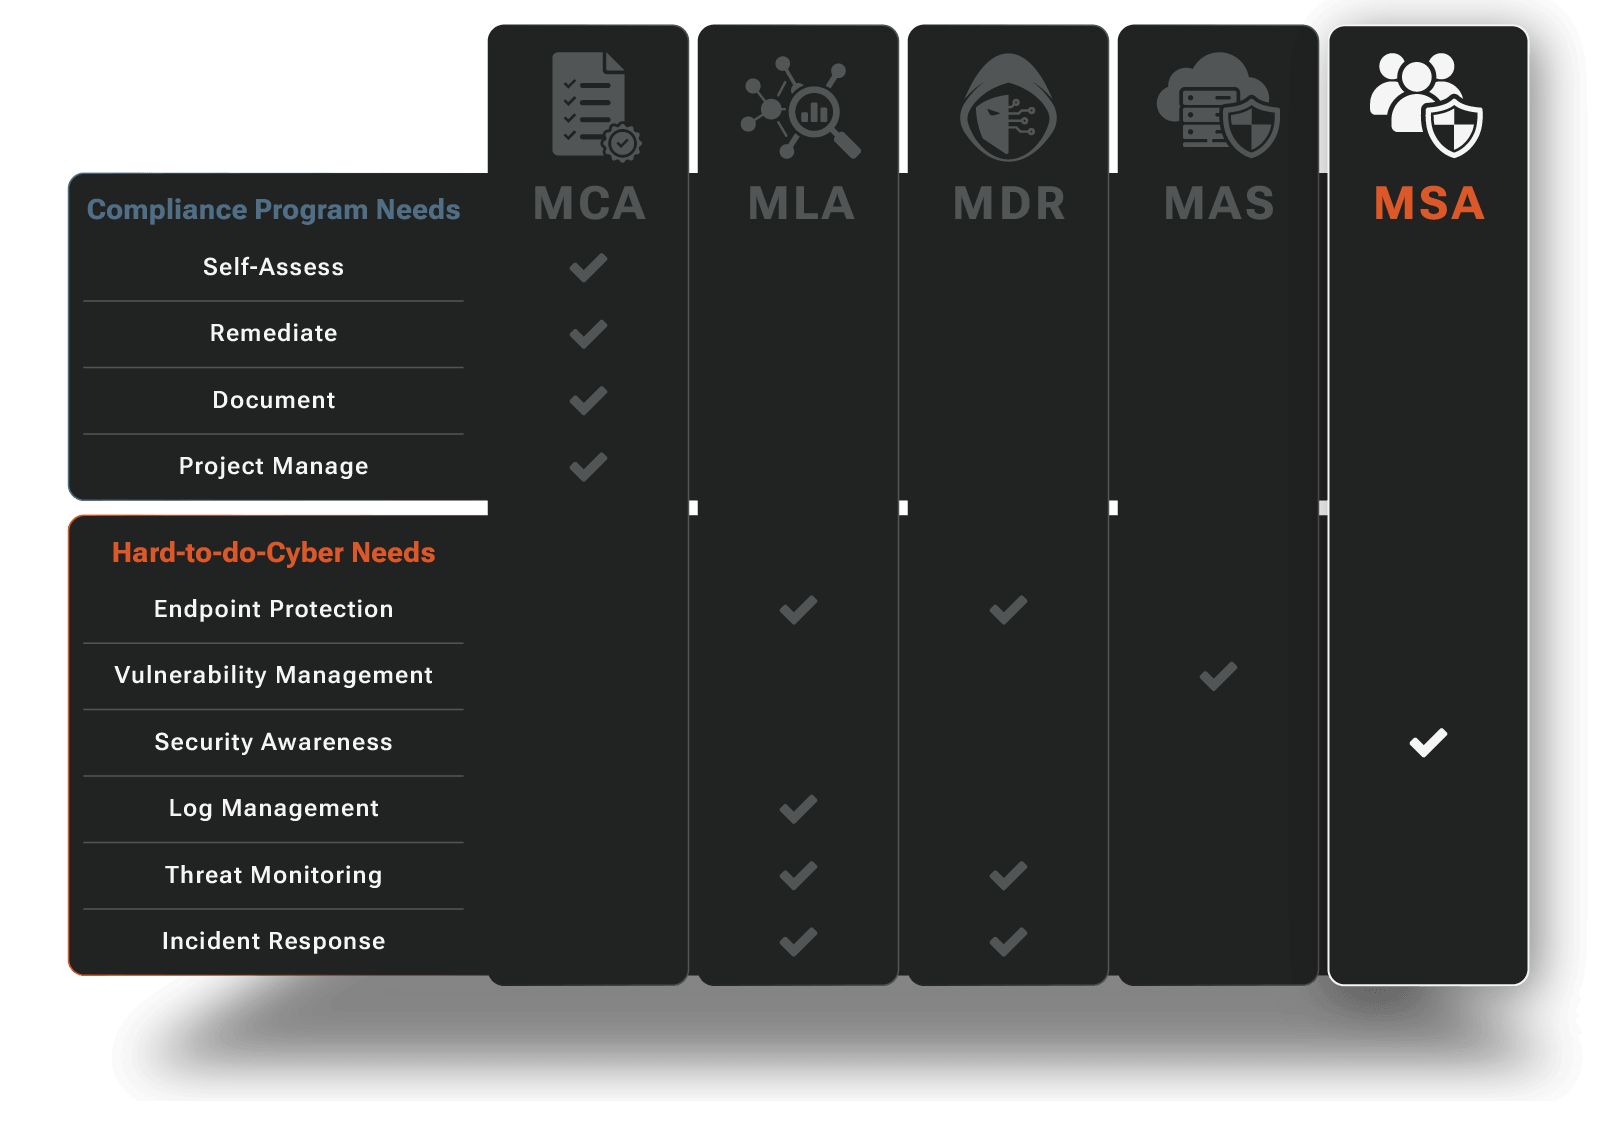
Our Solutions

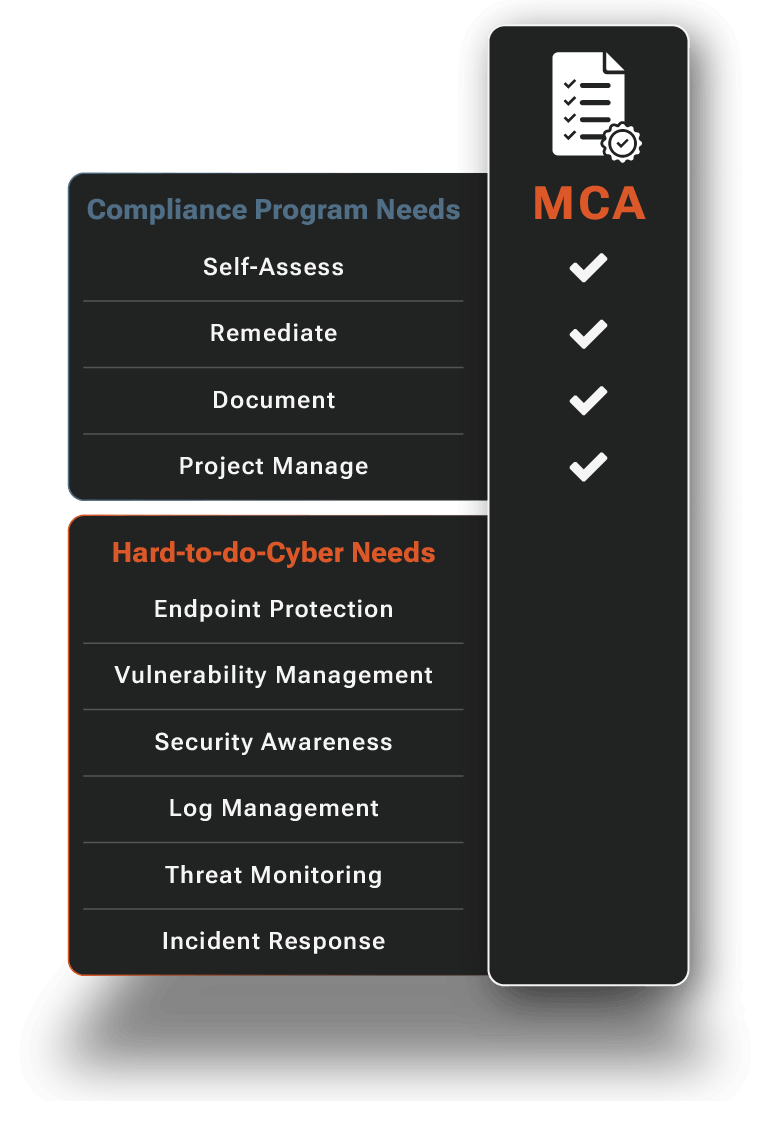
Managed Compliance Adherence drives your NCUA and NIST CSF program end to end, while our vSOC operates the hard-to-do security that most reduces cyber incident risk — together, a complete Cybersecurity-as-a-Service for credit unions.

Div Line_Desktop

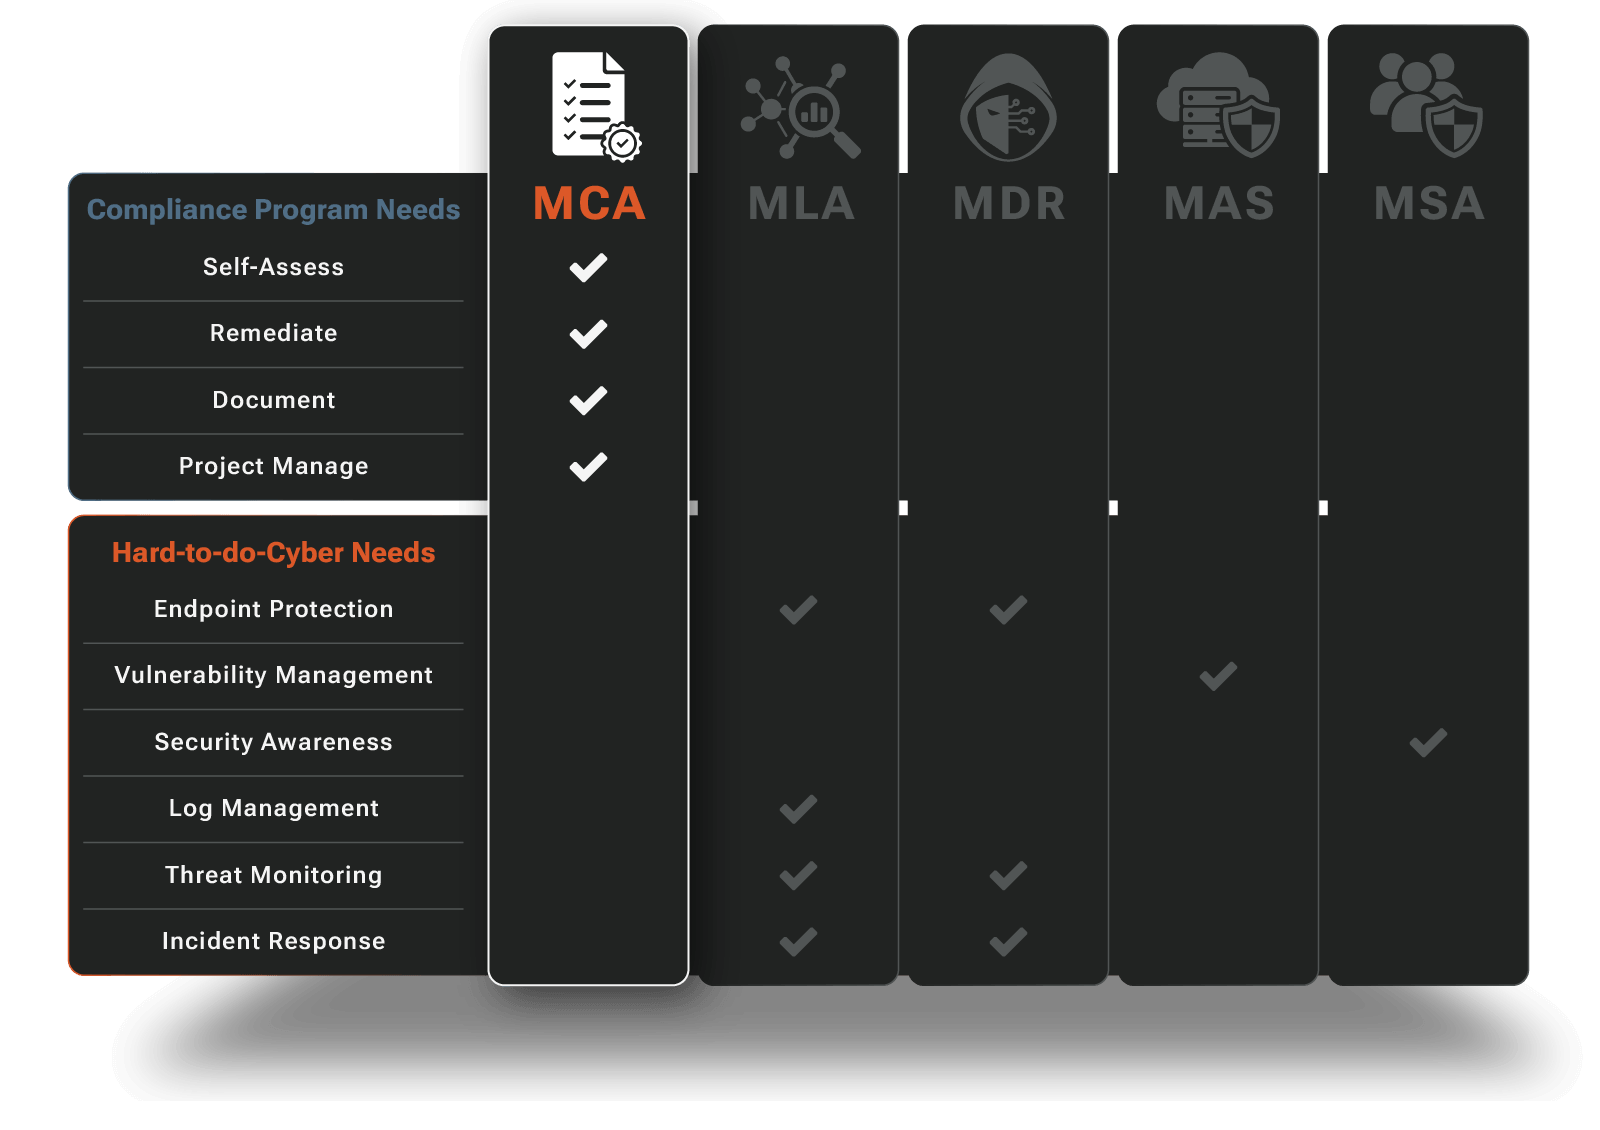
Managed Compliance Adherence

Drives your NCUA & NIST CSF compliance and verification program.

NCUA expectations and frameworks like NIST CSF are now a cost of doing business — we keep that cost low. Certified compliance experts combined with agentic automation fast-track readiness, reduce exam anxiety, and drive your program across all 106 CSF subcategories so your environment runs to the framework, not just claims to.

  • Guided self-assessments made easy
  • Audit trail and evidence capture
  • NCUA exam preparedness & efficiency
  • Compliance gaps quickly closed
  • Real-time compliance posture clarity
  • Jett AI clarifies requirements & drafts docs
RADICL_MCA Overview
Div Line_Desktop

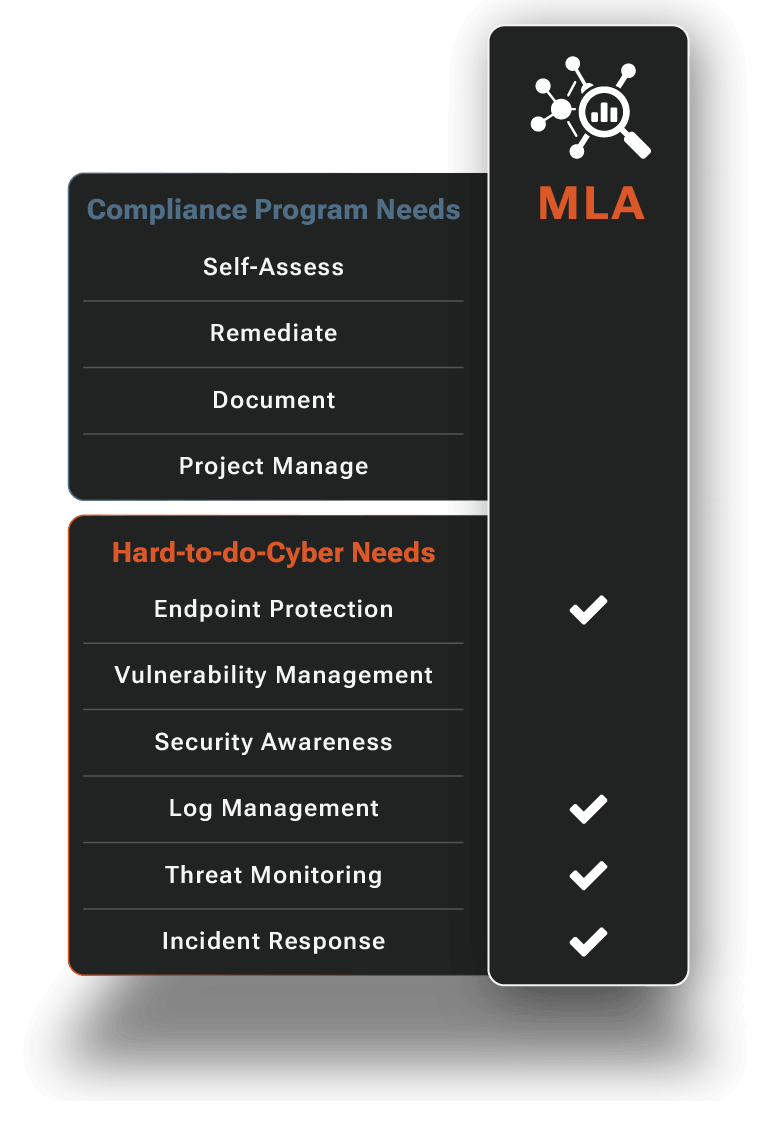
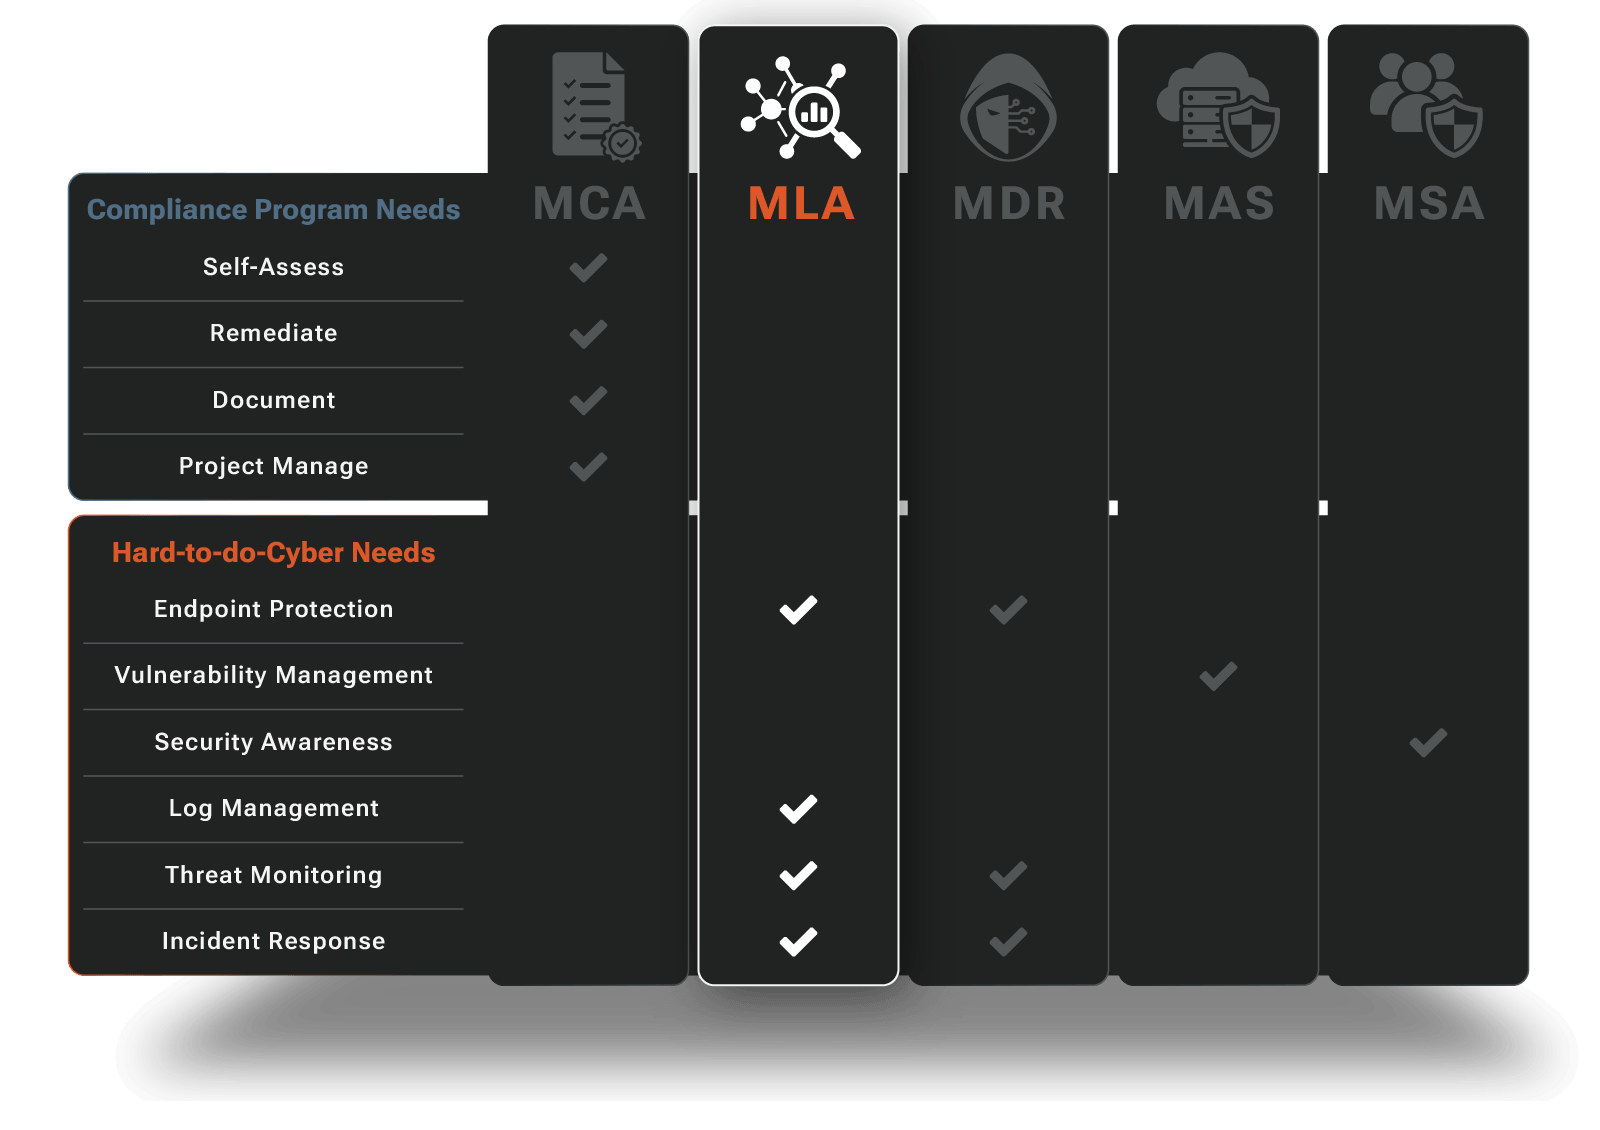
Managed Log Analytics

The log foundation for detection and NCUA exam evidence.

Investigations and exams require comprehensive visibility, but aggregating logs across your environment is complex and costly — not with us. We handle the full lifecycle from collection to searchable, long-term retention, giving you the evidence examiners ask for and the foundation detection depends on.

  • 14 or 90-day velocity search + 1-year archive
  • Hunt experience with vSOC escalation
  • vSOC-managed ingestion & health monitoring
  • AI-assisted natural-language search
  • On-demand compliance evidence export
  • Forensic search when an incident occurs
RADICL_MCA Overview
Div Line_Desktop

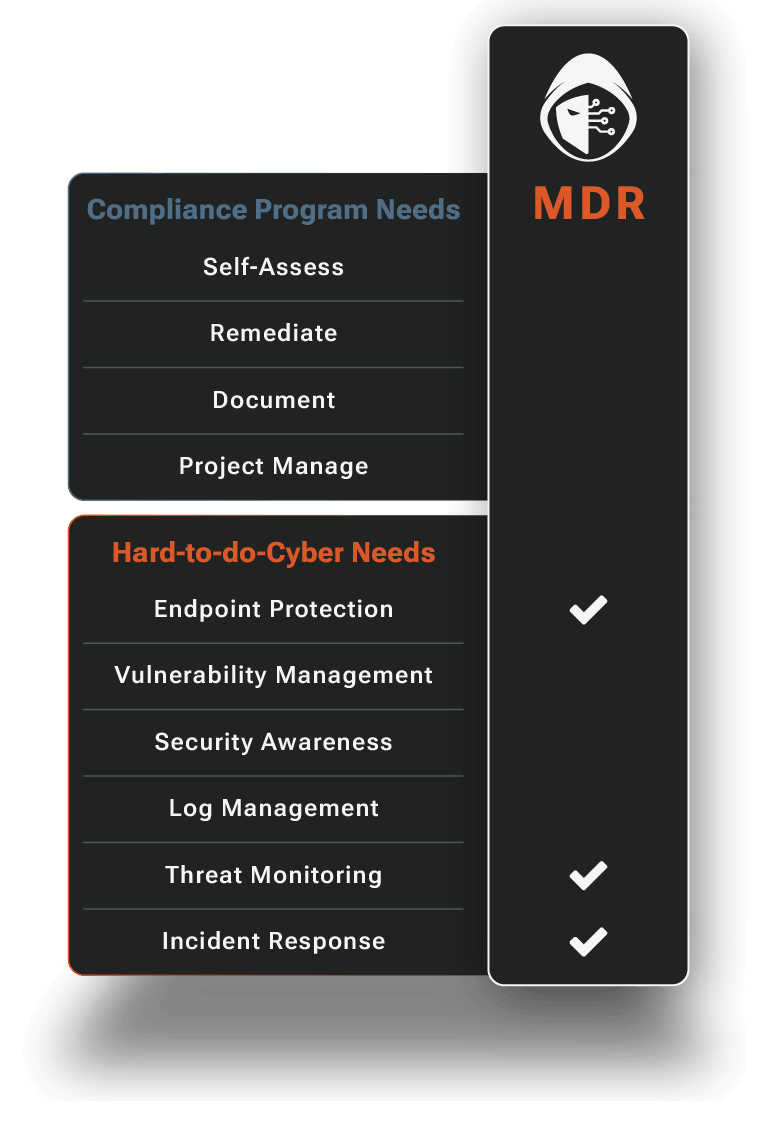
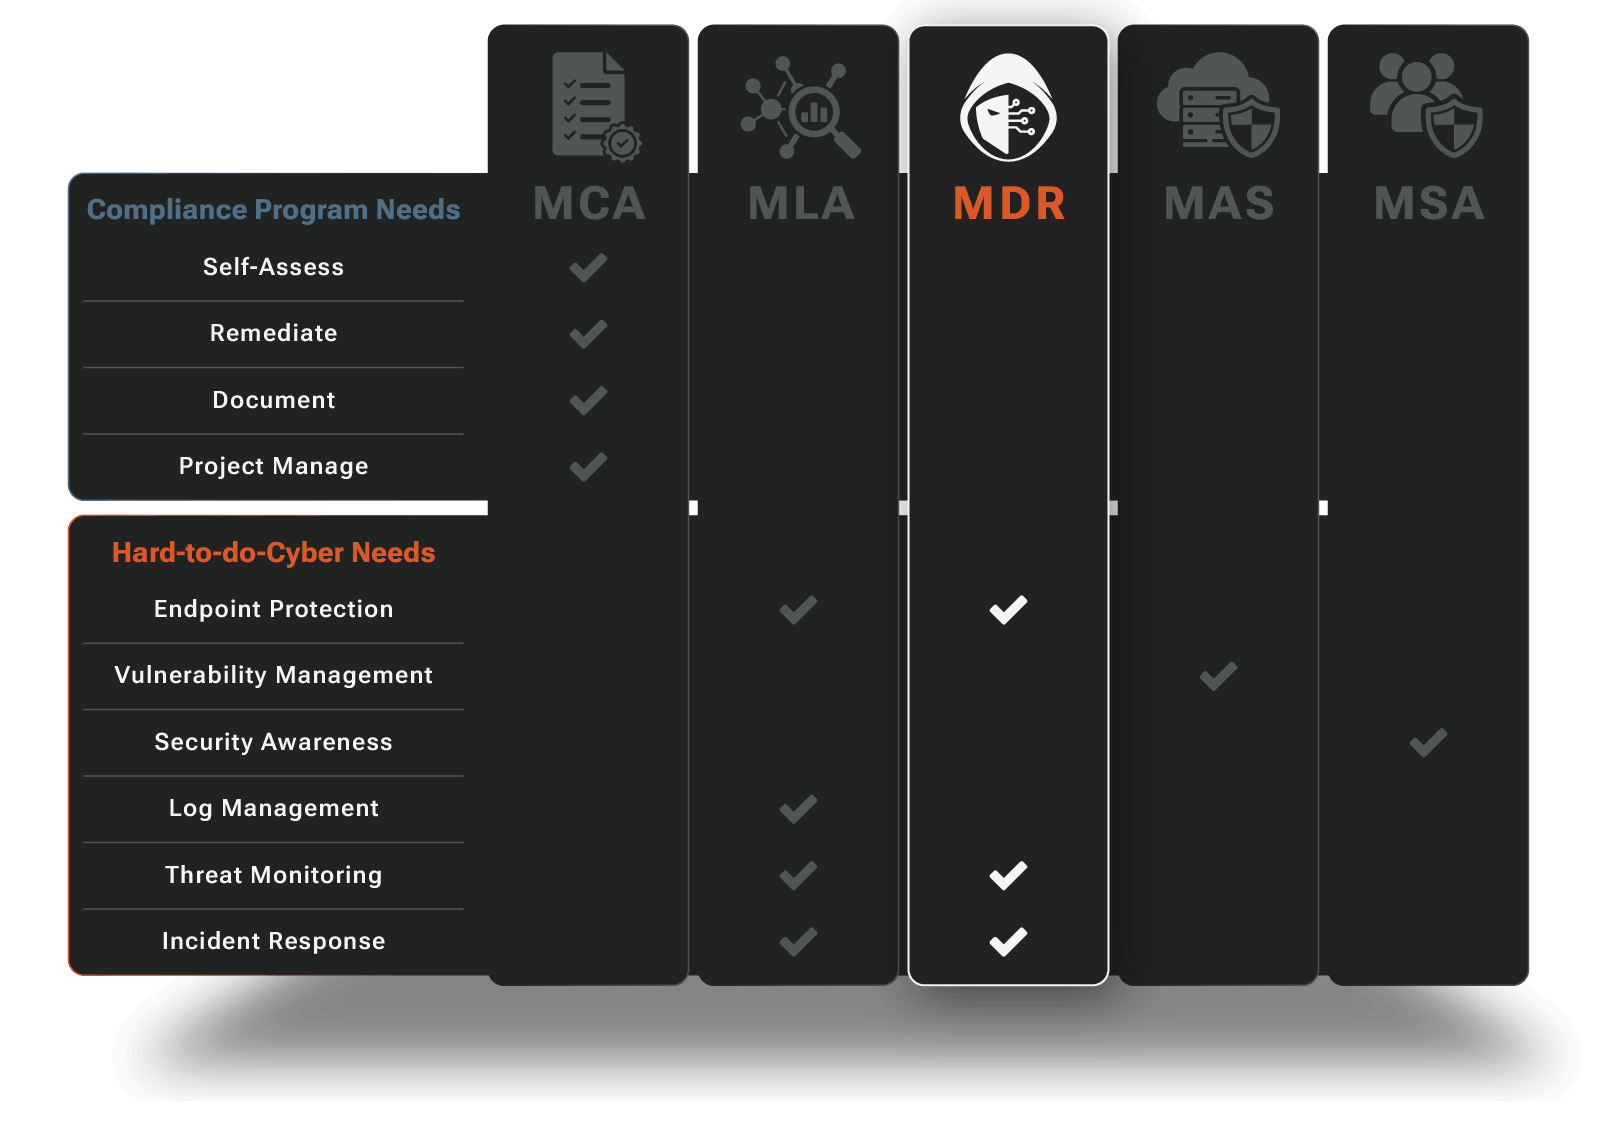
Managed Detection
and Response

24/7 monitoring, threat hunting, and end-to-end incident response.

Advanced endpoint protection, expert threat hunting, and 24/7 incident response keep your credit union safe from ransomware, account takeover, and financial fraud — and put you in position to meet the NCUA 72-hour notification rule with confidence.

  • Endpoints and servers protected
  • Evasive & embedded threats stopped
  • 24/7 security operations has your back
  • Incidents managed end-to-end
  • Virtual CISO by your side
  • Account-takeover & inbox-compromise detection
MDR: Endpoint

MDR: Endpoint is the foundation of our MDR offering. We deploy, optimize, and maintain leading EDR technologies (for example, CrowdStrike, SentinelOne, and Microsoft Defender) across your laptops, workstations, and server infrastructure. We deploy custom detection analytics to spot threats out-of-the box EDR miss.

MDR: Identity

With MDR: Identity, we ingest and analyze data from Identity and user activity data sources like Microsoft 365 and Google Workspace. We monitor authentication activity, access to sensitive data and files, and email behavior to detect account takeover, inbox compromise, and data exfiltration.

MDR: Network

MDR: Network collects alarms and threat data from physical, wireless and cloud network infrastructure. We correlate this with endpoint and identity telemetry to fully investigate suspicious behavior and provide defense‑in‑depth coverage.

How RADICL Detects and Responds

Below is a closer look at our Managed Detection and Response (MDR) operations. This is how we turn signals into 24/7 investigations, containment, and tracked remediation.

 
Stage
What We Do
What You Get
1
Signals In
Ingest endpoint, identity, infrastructure, and network telemetry.
Full visibility with guided onboarding and managed data operations.
2
DeepThreat™ Analytics
Apply continuous analytics using proprietary threat intelligence.
Detection of threats missed by standard vendor alerts.
3
DeepThreat™ Hunts
Conduct expert-led threat hunts across your environment.
Identification of hidden and stealthy threats.
4
Triage
Evaluate alerts to determine real risk.
Confidence that every alert is reviewed and validated.
5
Investigate
Analyze incidents and capture evidence.
Clear incident visibility with documented findings and history.
6
Execute and Coordinate Response
Contain threats and coordinate remediation.
Confidence that response is handled and actions are clearly owned.
7
Improve Resiliency
Apply learnings and implement proactive defenses.
Stronger security posture with tracked actions and audit-ready evidence.
Div Line_Desktop

Managed Attack Surface

Vulnerability management that shrinks your exposure.

Threat actors leverage vulnerabilities to get a foot in the door. Our Managed Attack Surface offering persistently reduces your exposure so your credit union becomes a much harder target for both opportunistic and targeted attacks.

  • Endpoint & server vulnerabilities prioritized
  • Accelerated critical-fix response
  • Closed-loop "fixed" visibility
  • Pragmatic, manageable remediation pace
  • Expert guidance with your IT / MSP
  • Continuous attack-surface reduction
RADICL_MCA Overview
Div Line_Desktop

Managed Security Awareness

Turn your staff into a strong human line of defense.

People are too often the weak link. We shore up your human line of defense with security awareness content, exercises, and phishing simulations informed by the real threats our vSOC sees every day — reducing the human-driven risk behind most incidents.

  • Comprehensive annual training
  • Phishing attack simulations
  • Security-awareness posture visibility
  • Ongoing "bite-sized" training
  • Ever-evolving expert content
  • Member-facing fraud-awareness ready
RADICL_MCA Overview

“The out-of-box experience exceeded what I saw in the demo, which is uncommon. During a CEO roundtable with over 100 credit union leaders, I was pleased to recommend RADICL.”


Nicole Smith | President & CEO at U S Federal Credit Union

“The out-of-box experience exceeded what I saw in the demo, which is uncommon. During a CEO roundtable with over 100 credit union leaders, I was pleased to recommend RADICL.”


Nicole Smith | President & CEO at U S Federal Credit Union

Get the Visibility You Deserve

Operational transparency is a core value. You'll know exactly what we're doing to keep your credit union secure and compliant — because through transparency comes accountability and trust, the same values credit unions are built on.


Your Protection Delivered dashboard gives credit union leadership and your board real-time visibility into how RADICL is defending members every day — the proof points you can bring straight into a board meeting or an NCUA exam.

Our Protection Delivered Dashboard

Watch this video to learn how with RADICL, you'll enjoy real-time visibility into how we are:

Let's keep your members' finances safe

Tell us about your credit union and we'll scope the right level of coverage — driving your NCUA compliance while operating the hard-to-do cyber that most reduces incident risk. No overbuying, no complexity.

Talk to a specialist Call (720) 738-7529

Frequently Asked Questions

What NCUA cybersecurity requirements apply to credit unions?

Every federally insured credit union must maintain a written information security program under NCUA Part 748 (which implements the GLBA Safeguards requirements), and since September 2023 must notify the NCUA within 72 hours of reasonably believing a reportable cyber incident has occurred — including incidents that originate with a third-party vendor. The NCUA's Information Security Examination (ISE) program tests your controls and evidence, and with the FFIEC Cybersecurity Assessment Tool retired, examiners increasingly expect programs mapped to a recognized framework like NIST CSF 2.0. RADICL drives that program and maintains the evidence you need.

Does a credit union our size really need a SOC?

Not one you build yourself. Standing up 24/7 security operations internally requires staffing, tooling, and ongoing investment that's out of reach for most credit unions, especially those with a one- or two-person IT team. RADICL's vSOC model gives you the same round-the-clock detection, triage, and response leadership you'd get from an internal SOC, without the overhead or expense of building and running one.

Our MSP says they handle security. Isn't that enough?

Your MSP keeps you running; that's essential, but different from cybersecurity. Most MSPs aren't staffed to run a 24/7 SOC, hunt for evasive threats, or drive a compliance program against NCUA expectations. RADICL overlays managed security and compliance on top of your MSP, handles the specialized work, and hands off precise remediation tasks — so you keep the partner you trust while closing the gap they weren't built to cover.

Why one partner instead of best-of-breed tools?

Piecing together a SIEM, EDR, vulnerability scanner, and training platform from different vendors drives up cost and complexity — and creates gaps between tools that no one owns. RADICL delivers detection and response, log analytics, vulnerability management, security awareness, and compliance as one integrated Cybersecurity-as-a-Service, operated by one team through one platform. Strong cybersecurity, simplified.

How do you help with the NCUA 72-hour notification rule?

RADICL owns incident response end to end — triage, investigation, mitigation, and recovery — and our Managed Log Analytics gives you the searchable, retained evidence to scope and document an incident quickly. That means when the clock starts, you can determine what happened, contain it, and produce the documentation to notify the NCUA inside the window.

What proof do we get for our board and examiners?

You get current, audit-ready evidence: a NIST CSF-aligned program with captured notes and screenshots, centralized log evidence with a one-year archive, verified vulnerability remediation, and documented incident-response outcomes — all consolidated in-platform. Instead of scrambling before an exam or a board meeting, the proof is maintained continuously and available on demand, including a real-time posture dashboard your directors can read.

How quickly can we get protected?

Because we're not starting from scratch — no hiring, no tool procurement, no lengthy custom build — most credit unions can have core telemetry ingestion, monitoring, and evidence workflows operational in weeks, not months, with a phased approach available as you expand coverage.