

Cybersecurity for the Nuclear Sector

Protect High-Consequence Operations. Operate the Hard Controls. Prove the Work.

RADICL provides Virtual Security Operations Center (vSOC)-led managed cybersecurity for nuclear-sector organizations and their supply chain, including component manufacturers, engineering firms, and new-build and advanced-reactor developers.
Talk to a Specialist Learn About Our Platform
  • ACS

  • Aerial Machine & Tool

  • Agile Space Industries

  • Anew Solutions

  • Barn Owl Tech

  • Blue Sky Innovators

  • C Speed

  • DLZ

  • Electra Aereo

  • Firehawk Aerospace

  • G&H

  • Havoc AI

  • HTX Labs

  • Miltope

  • MAK Technologies

  • Red6

  • SpektreWorks

  • Stonhard: Commercial & Industrial Flooring

  • Trenton Systems

  • Urban Sky

  • VATN Systems

  • Zone5 Technologies

What Is Nuclear Cybersecurity?

Nuclear cybersecurity protects the digital systems, networks, identities, and data used across the nuclear sector. This can include corporate and engineering IT, cloud services, email and identity systems, sensitive technical data, supplier connections, and supported telemetry where business networks meet operational technology (OT).

Nuclear power plant cybersecurity also contains a specialized regulatory layer. For operating power reactors, NRC requirements protect digital systems associated with safety, security, and emergency-preparedness functions. The NRC notes that systems that monitor and control safety functions are isolated from external communications, including the internet, to prevent unauthorized access.

We help lean teams protect sensitive corporate and engineering environments, respond to threats, reduce vulnerabilities, and maintain defensible evidence.

Your team gets continuous security coverage without building and staffing an in-house enterprise SOC.

Div Line_Desktop
Div Line_Mobile

Why the Nuclear Sector Is a High-Value Cyber Target

Nuclear organizations work with high-value technology, sensitive engineering information, critical infrastructure, and complex supply chains. This creates security concerns well beyond the plant itself.

Nation-State & Geopolitical Interest

Nation-State & Geopolitical Interest

Nuclear technology, fuel-cycle work, and new-build programs can attract sophisticated adversaries seeking intellectual property, sensitive information, or persistent access.
Sensitive Designs & Nuclear Data

Sensitive Designs & Nuclear Data

Depending on the organization, valuable information can include engineering designs, proprietary technical data, export-controlled information, or other protected nuclear information.
Supply-Chain & Flowdown Risk

Supply-Chain & Flowdown Risk

Manufacturers, engineering firms, developers, and service providers may inherit security expectations through operators, primes, federal contracts, and other customer requirements.
Lean Teams Behind High-Consequence Work

Lean Teams Behind High-Consequence Work

Suppliers and developers may support demanding programs with relatively small security teams, making continuous monitoring, investigation, and evidence difficult to sustain.
What Cybersecurity Requirements Apply to Nuclear Organizations?

Applicability depends on your role in the nuclear sector, licensing pathway, systems, contracts, and other regulatory obligations.

Power reactor licensees can face NRC cybersecurity requirements. Applicable Bulk Electric System functions can involve NERC CIP. Suppliers and developers may also encounter NIST requirements through federal contracts.

NIST SP 800-171 Services NIST Compliance Services
Div Line_Desktop
Div Line_Mobile

Where Lean Nuclear-Sector Teams Get Stuck

Lean nuclear-sector teams can support high-consequence work while managing security with limited internal resources.

No practical 24/7 coverage

No practical 24/7 coverage

Small teams cannot continuously monitor and investigate security activity while also managing IT and daily operations.
Evidence and review burden

Evidence and review burden

Security work never stops, but records scatter across tickets, email, and portals until a customer or regulator asks for proof.
Icon-240

IT/OT boundary blind spots

Visibility, telemetry, and response ownership can become inconsistent where corporate networks meet operational environments.
Supply-chain obligations

Supply-chain obligations

Security requirements flow down from operators, primes, and contracts, while vendors add access paths and shared responsibilities.
Alert and vulnerability overload

Alert and vulnerability overload

Security tools can generate more findings than lean teams have time to investigate, prioritize, remediate, and verify.
Unclear response authority

Unclear response authority

During an incident, IT, leadership, vendors, MSPs, and other stakeholders may not know who can isolate, restore, report, or communicate.
The Hardest Cybersecurity Controls for Nuclear-Sector Organizations

The hardest security activities are often those that must run continuously. For suppliers, developers, and other nuclear-sector organizations, logging, response, vulnerability management, and awareness all require ongoing ownership.

Log Management

Log Management

Security telemetry has to remain collected, searchable, retained, and available when an investigation or review begins. Gaps can limit both response and supporting evidence.
Incident Response

Incident Response

Teams need defined roles, escalation paths, communication procedures, and decision authority before an incident occurs. Exercises can expose gaps while there is still time to fix them.
Vulnerability Management

Vulnerability Management

Identifying vulnerabilities is only the beginning. Teams still need to account for asset importance, exploitability, vendor dependencies, operating constraints, and remediation progress.
Security Awareness

Security Awareness

Employees, engineers, administrators, and contractors need practical preparation for phishing, credential theft, social engineering, and other threats targeting trusted access.

Options for Nuclear-Sector Organizations

The right starting point depends on your role in the sector, systems, contractual scope, and operational constraints.

Path
What It Covers
Best for
Corporate IT & Sensitive-Data Path
Focus security operations and evidence on the corporate and engineering environment where identities, email, cloud services, designs, project data, and controlled information live.
Suppliers, engineering firms, and developers whose primary exposure is corporate IT, engineering systems, and intellectual property
IT/OT Boundary Path
Establish visibility and response around supported telemetry where corporate networks meet operational environments. Plant-specific control systems remain under the appropriate OT and regulatory programs.
Organizations that need stronger visibility around network boundaries without extending general-purpose endpoint tooling into specialized control environments.
Supply-Chain / Scoped Readiness Path
Focus security operations and supporting evidence on a defined set of systems affected by customer, prime, or contractual security requirements.
Teams that need to demonstrate readiness across a specific customer, project, enclave, or contractual scope.

Our Solutions

Div Line_Desktop

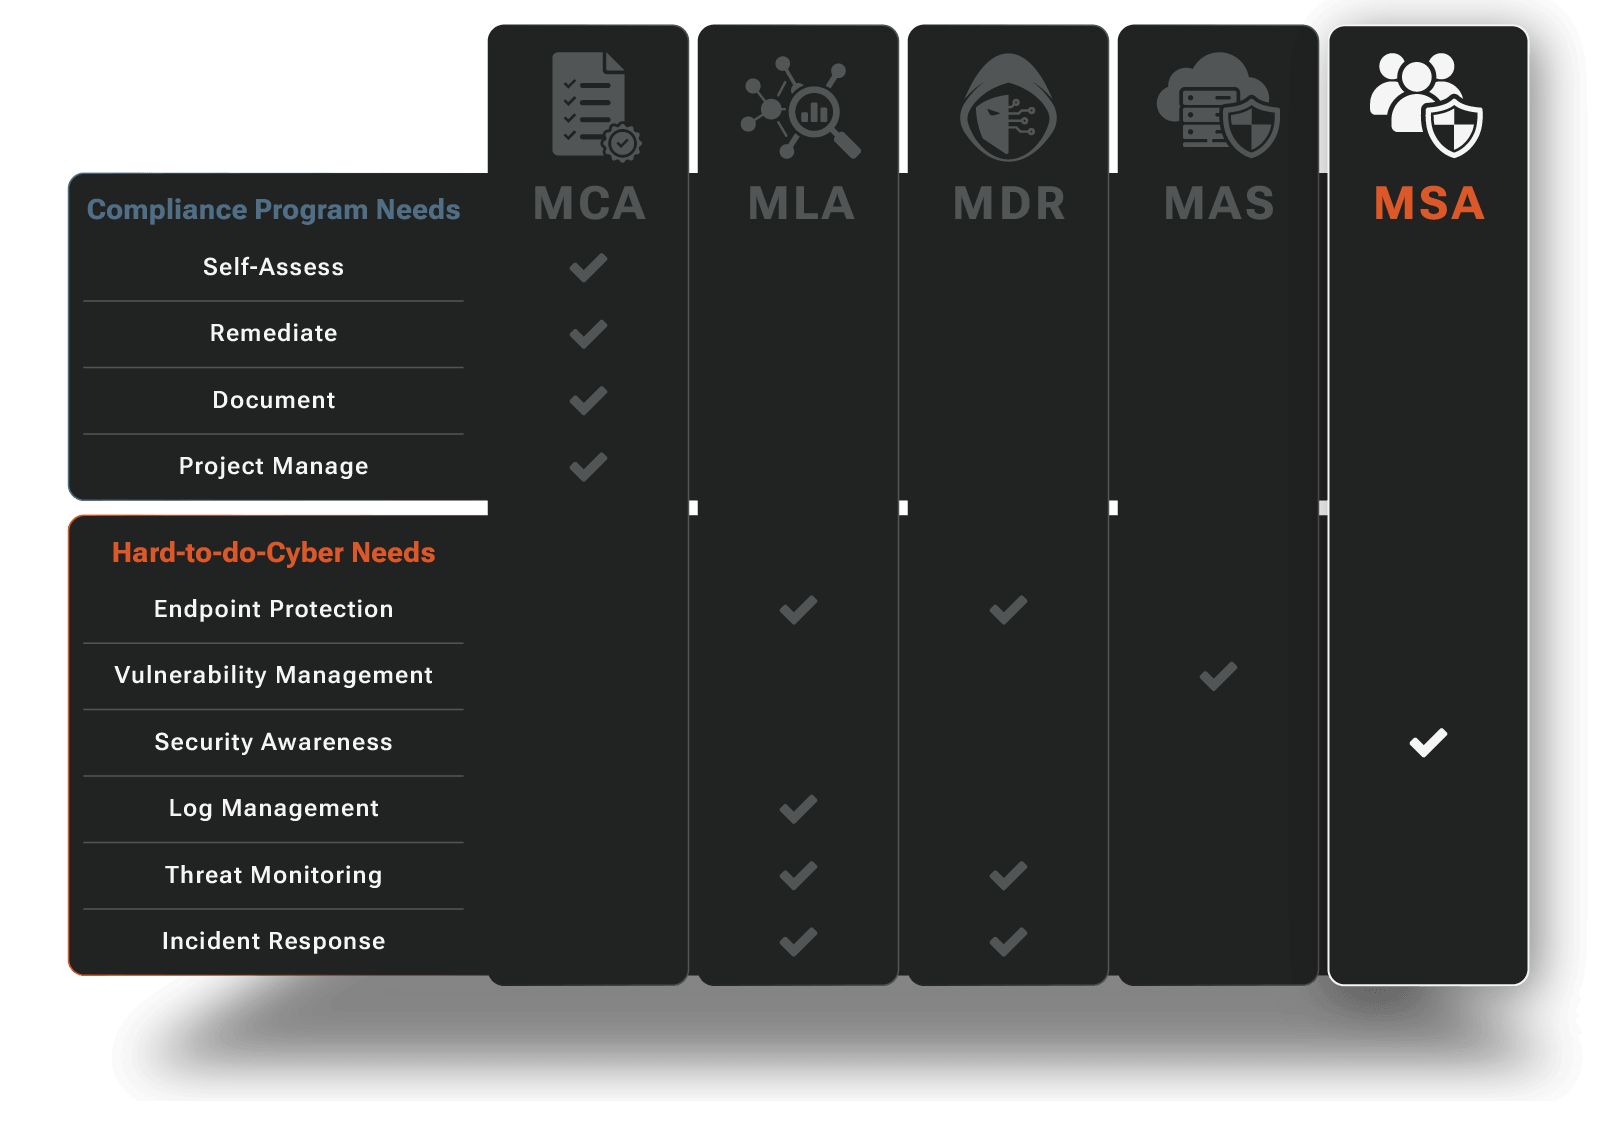
Managed Detection
and Response

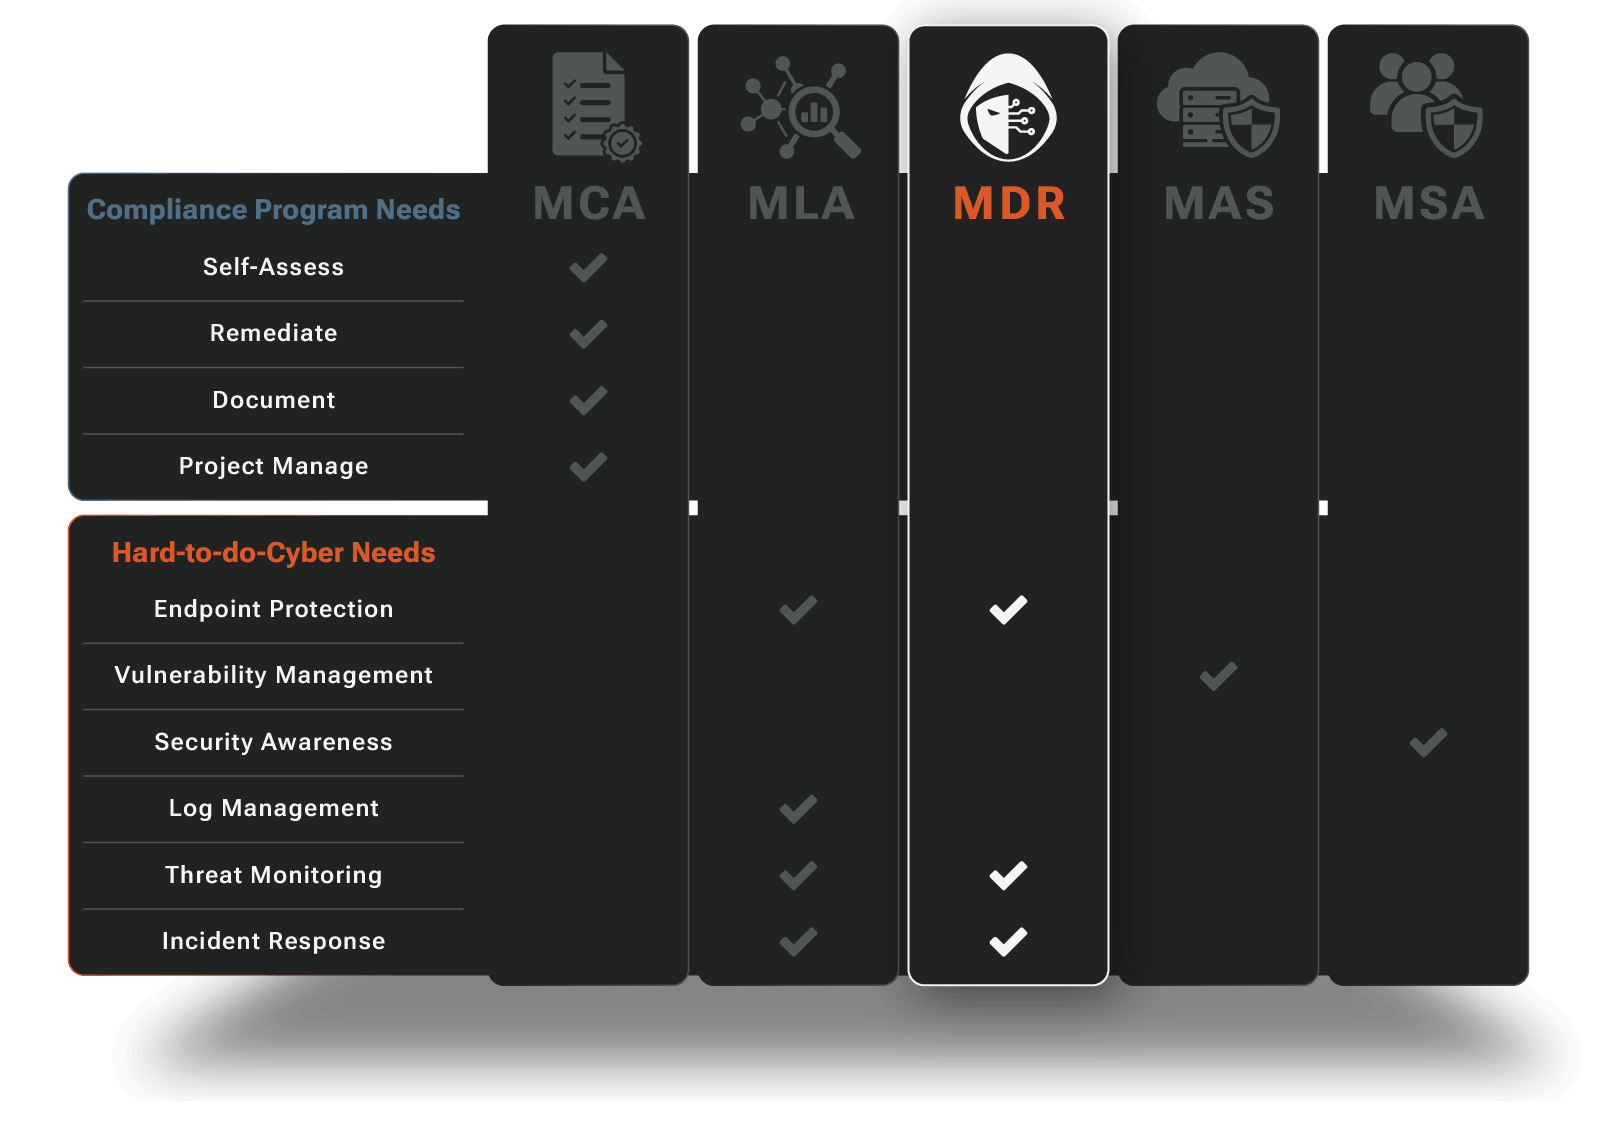
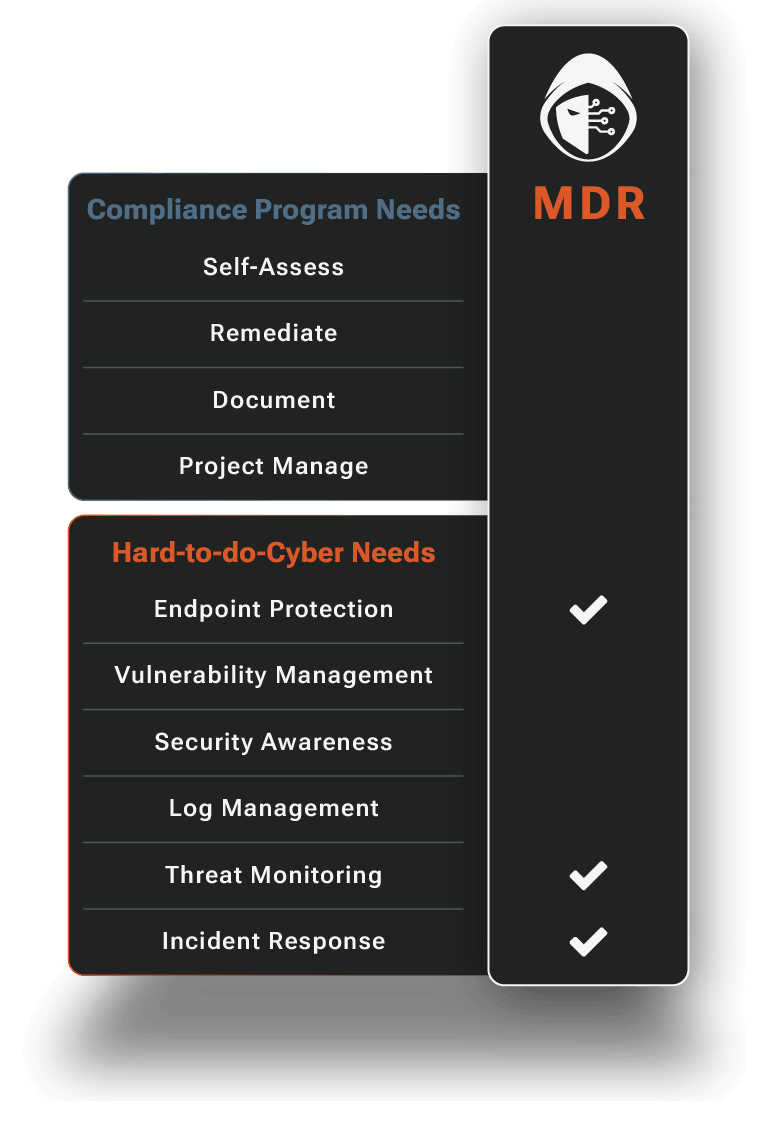
Managed Detection and Response (MDR) provides 24/7 monitoring, investigation, threat hunting, supported containment, and coordinated response across covered endpoint, identity, and network environments.

RADICL's vSOC combines security expertise with AI-assisted workflows so lean teams can maintain continuous coverage without staffing a full internal SOC.

  • Endpoints and Servers Protected
  • Evasive & Embedded Threats Detected and Stopped
  • 24/7 Security Operations Has Your Back
  • Incidents Managed End-to-End
  • Virtual CISO By Your Side

MDR: Endpoint

MDR: Endpoint is the foundation of our MDR offering. We deploy, optimize, and maintain leading EDR technologies (for example, CrowdStrike, SentinelOne, and Microsoft Defender) across your laptops, workstations, and server infrastructure. We deploy custom detection analytics to spot threats out-of-the box EDR miss.

MDR: Identity

With MDR: Identity, we ingest and analyze data from Identity and user activity data sources like Microsoft 365 and Google Workspace. We monitor authentication activity, access to sensitive data and files, and email behavior to detect account takeover, inbox compromise, and data exfiltration.

MDR: Network

MDR: Network collects alarms and threat data from physical, wireless and cloud network infrastructure. We correlate this with endpoint and identity telemetry to fully investigate suspicious behavior and provide defense‑in‑depth coverage.

How RADICL Detects and Responds

Below is a closer look at our Managed Detection and Response (MDR) operations. This is how we turn signals into 24/7 investigations, containment, and tracked remediation.

 
Stage
What We Do
What You Get
1
Signals In
Ingest endpoint, identity, infrastructure, and network telemetry.
Full visibility with guided onboarding and managed data operations.
2
DeepThreat™ Analytics
Apply continuous analytics using proprietary threat intelligence.
Detection of threats missed by standard vendor alerts.
3
DeepThreat™ Hunts
Conduct expert-led threat hunts across your environment.
Identification of hidden and stealthy threats.
4
Triage
Evaluate alerts to determine real risk.
Confidence that every alert is reviewed and validated.
5
Investigate
Analyze incidents and capture evidence.
Clear incident visibility with documented findings and history.
6
Execute and Coordinate Response
Contain threats and coordinate remediation.
Confidence that response is handled and actions are clearly owned.
7
Improve Resiliency
Apply learnings and implement proactive defenses.
Stronger security posture with tracked actions and audit-ready evidence.
Div Line_Desktop

Managed Log Analytics

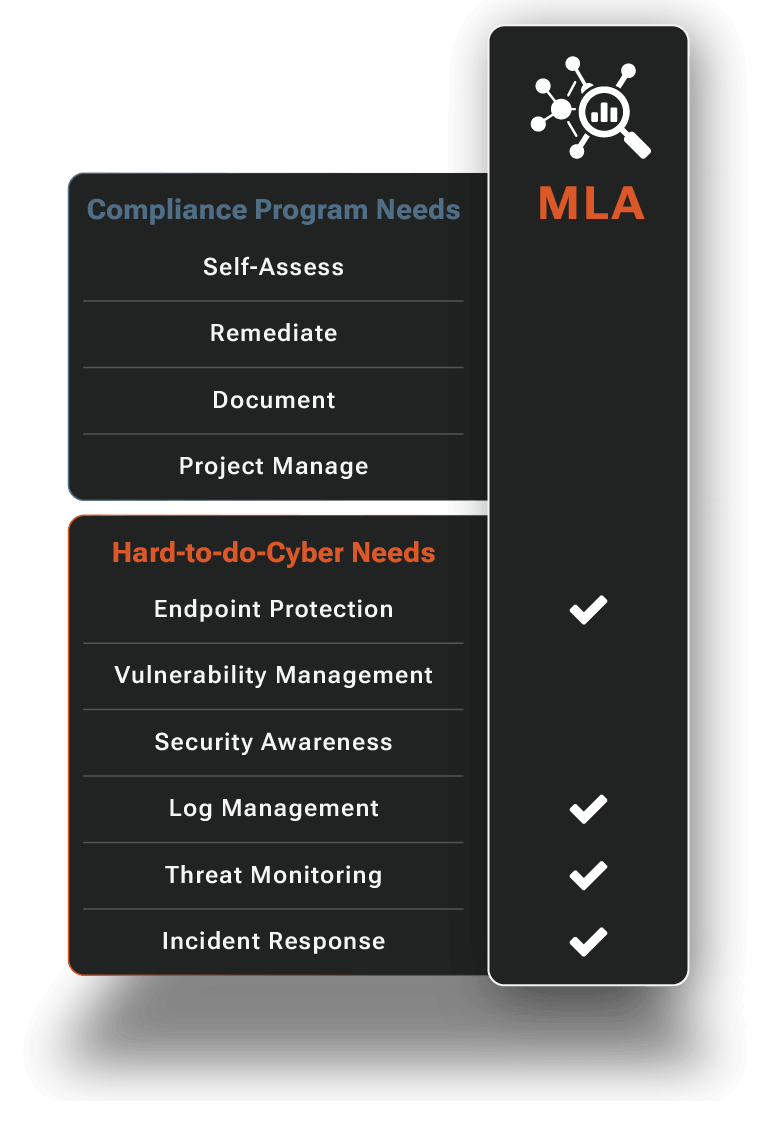
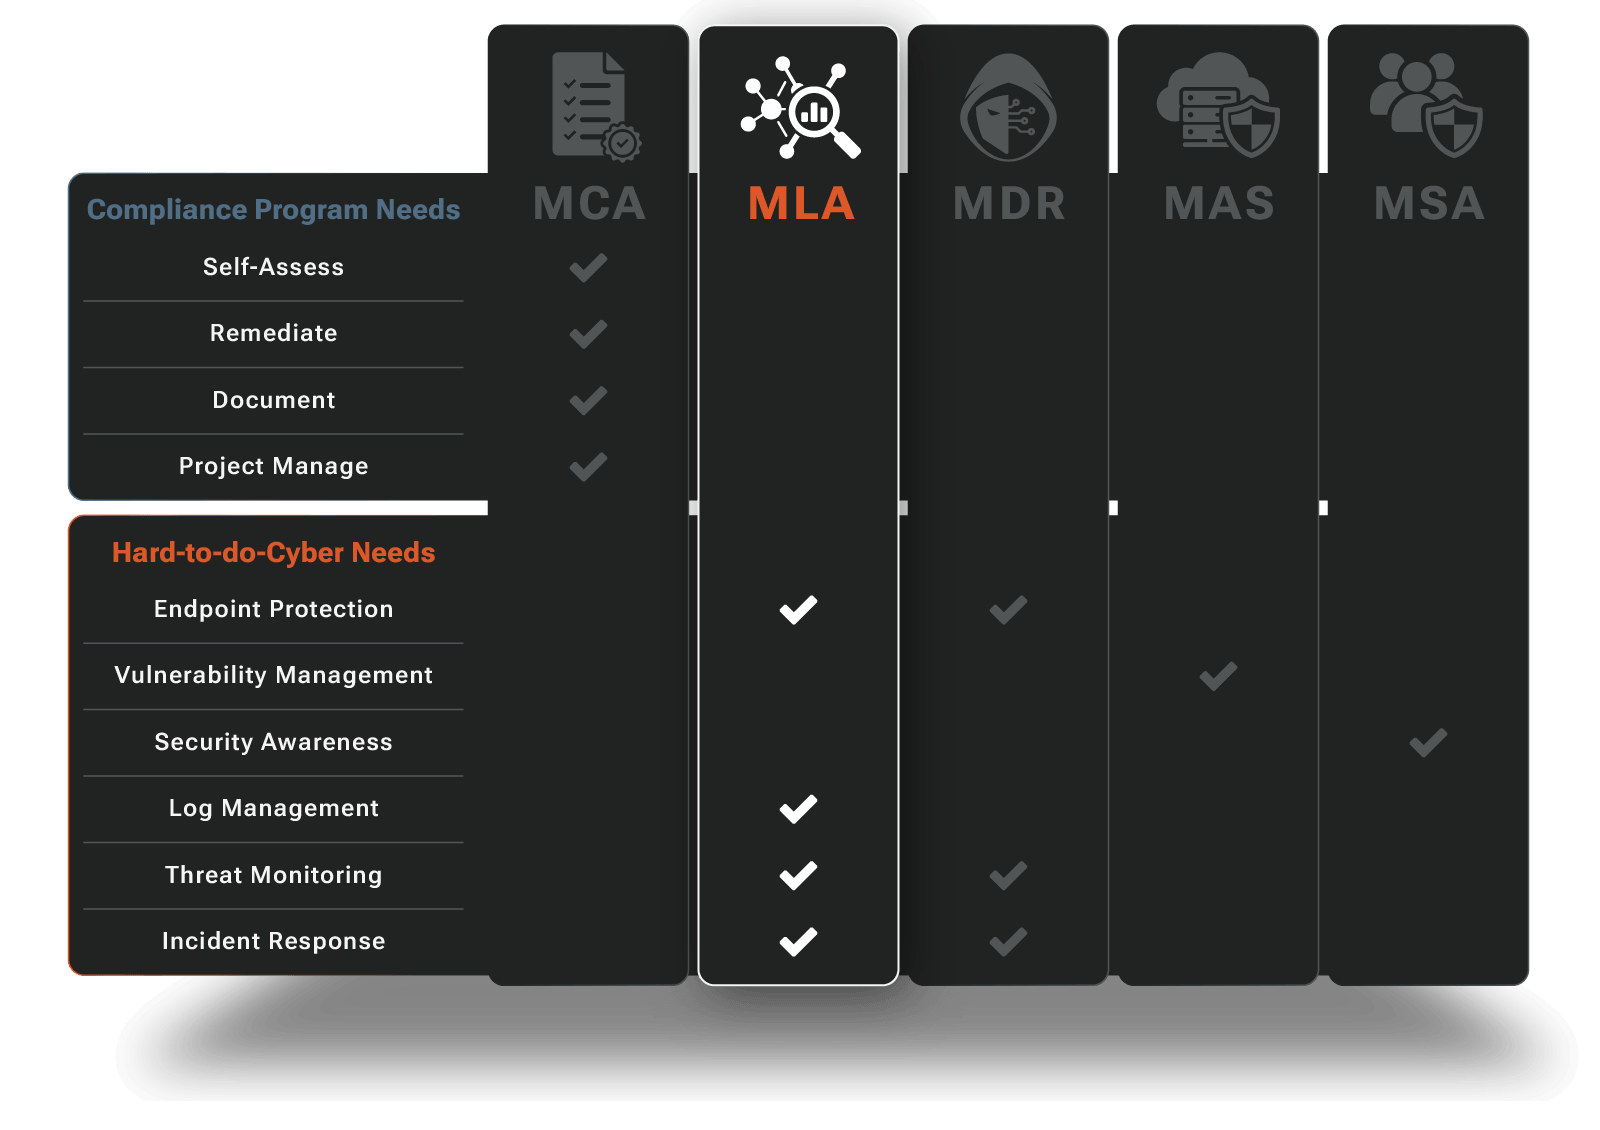
Managed Log Analytics (MLA) centralizes supported logs with managed collection, normalization, search, retention, and ingestion-health monitoring. Teams can use 14- or 90-day active search and a one-year archive for investigations and applicable evidence needs.

  • 14 or 90-Day Velocity Search + 1-Year Archive
  • AI-Assisted Natural Language Search
  • Hunt UX with vSOC Incident Escalation
  • On-Demand Compliance Evidence Export
  • vSOC-Managed Ingestion & Health Monitoring
RADICL_MCA Overview
Div Line_Desktop

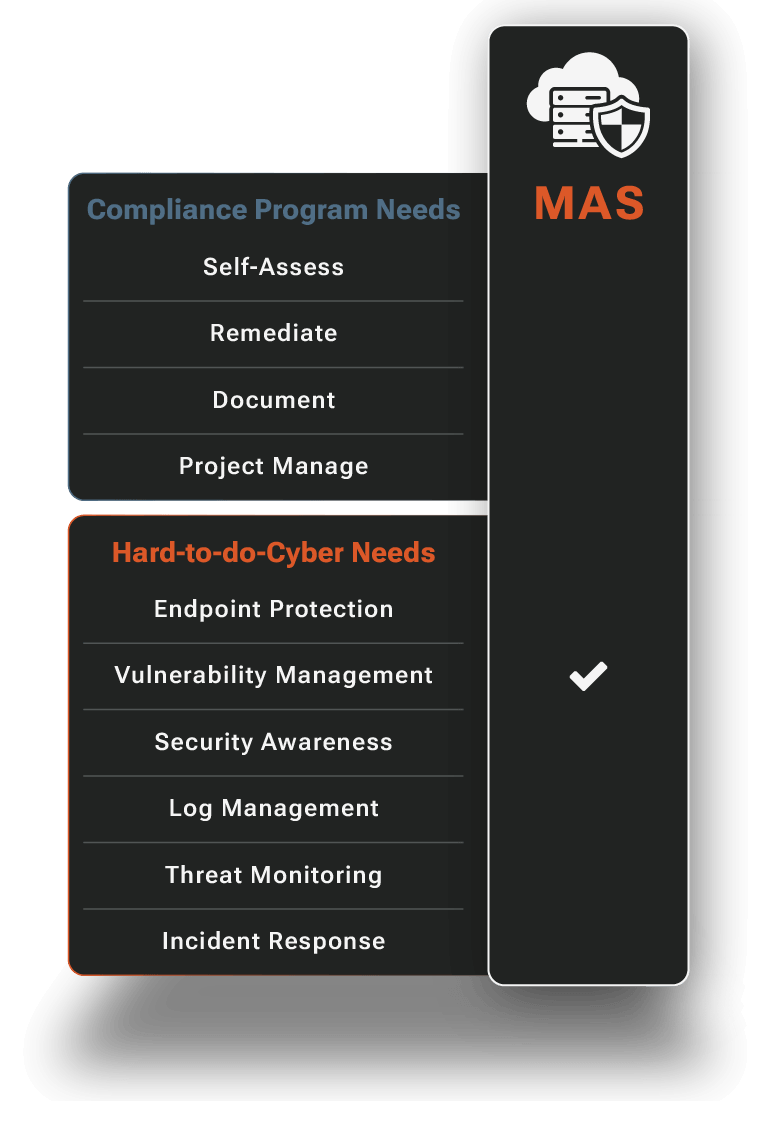
Managed Attack Surface

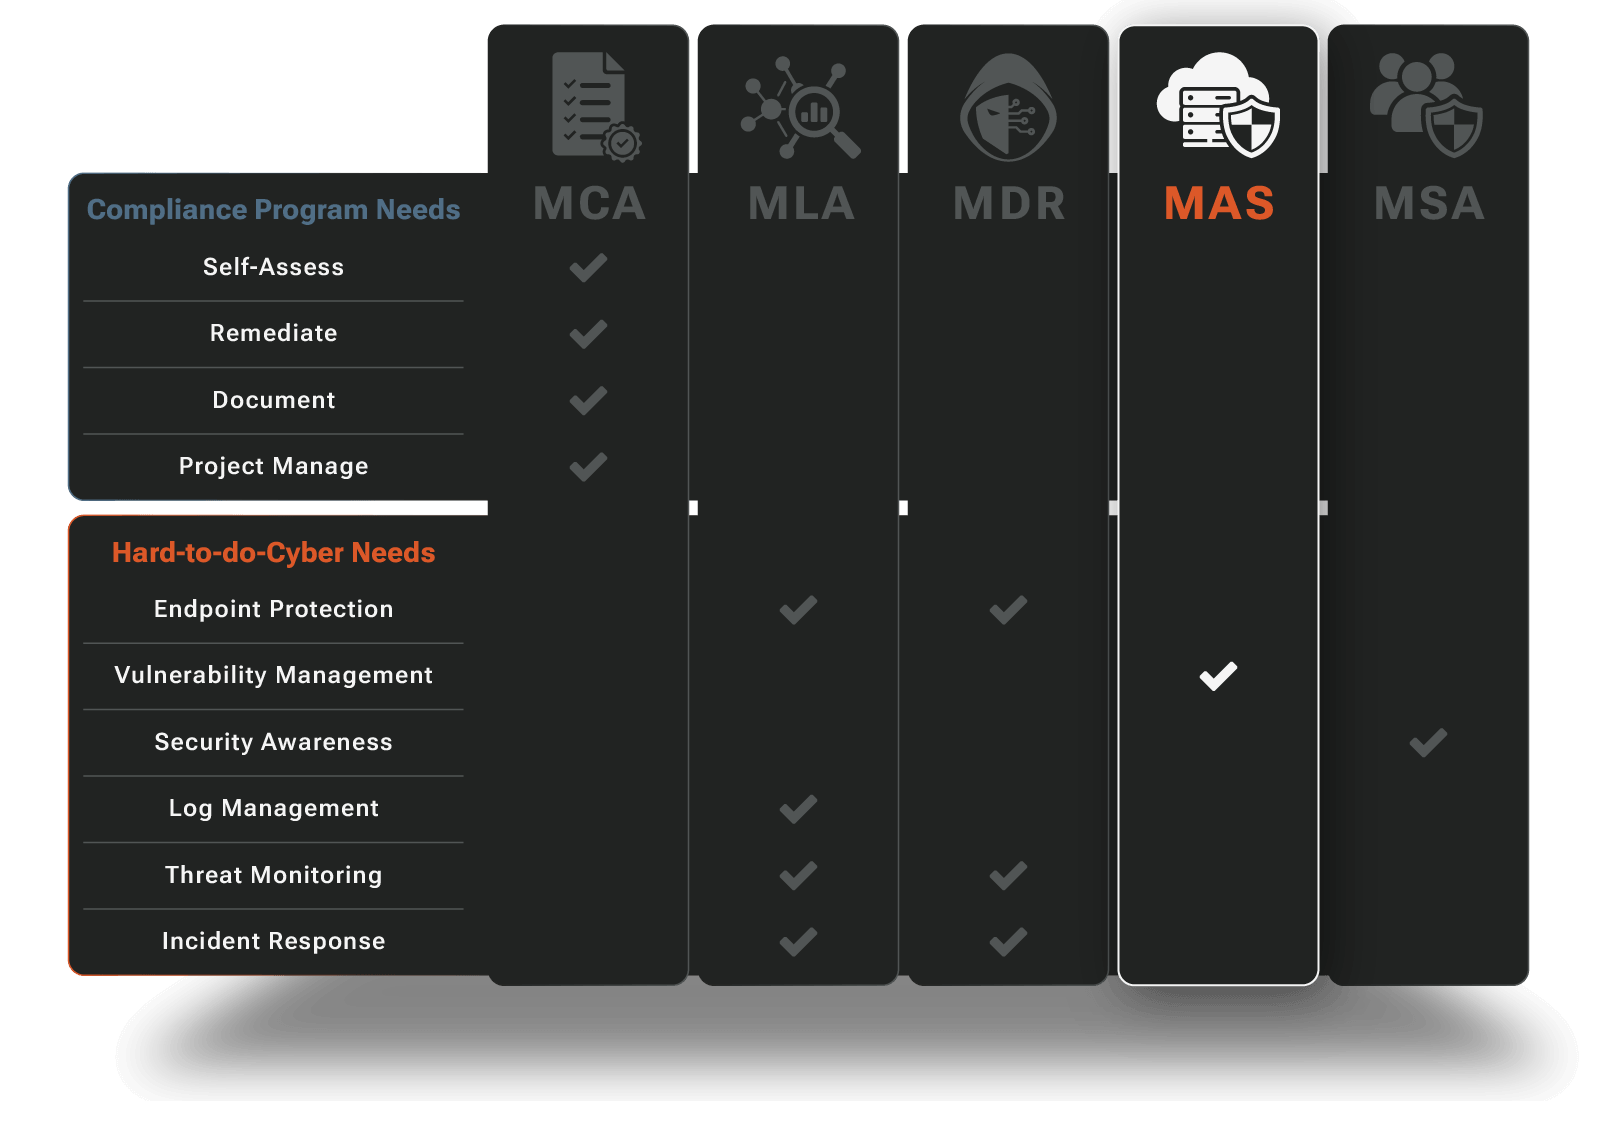
Managed Attack Surface (MAS) continuously identifies and prioritizes vulnerabilities using technical and business context. RADICL provides remediation guidance, tracks progress, and verifies reported closure.

  • Endpoint and Server Vulnerabilities Detected and Prioritized
  • Pragmatic and Manageable Remediation Pace
  • Accelerated Critical Fix Response
  • Expert Guidance and Collaboration With Your IT/MSP Partners
  • Closed Loop “Fixed” Visibility
RADICL_MCA Overview
Div Line_Desktop

Managed Security Awareness

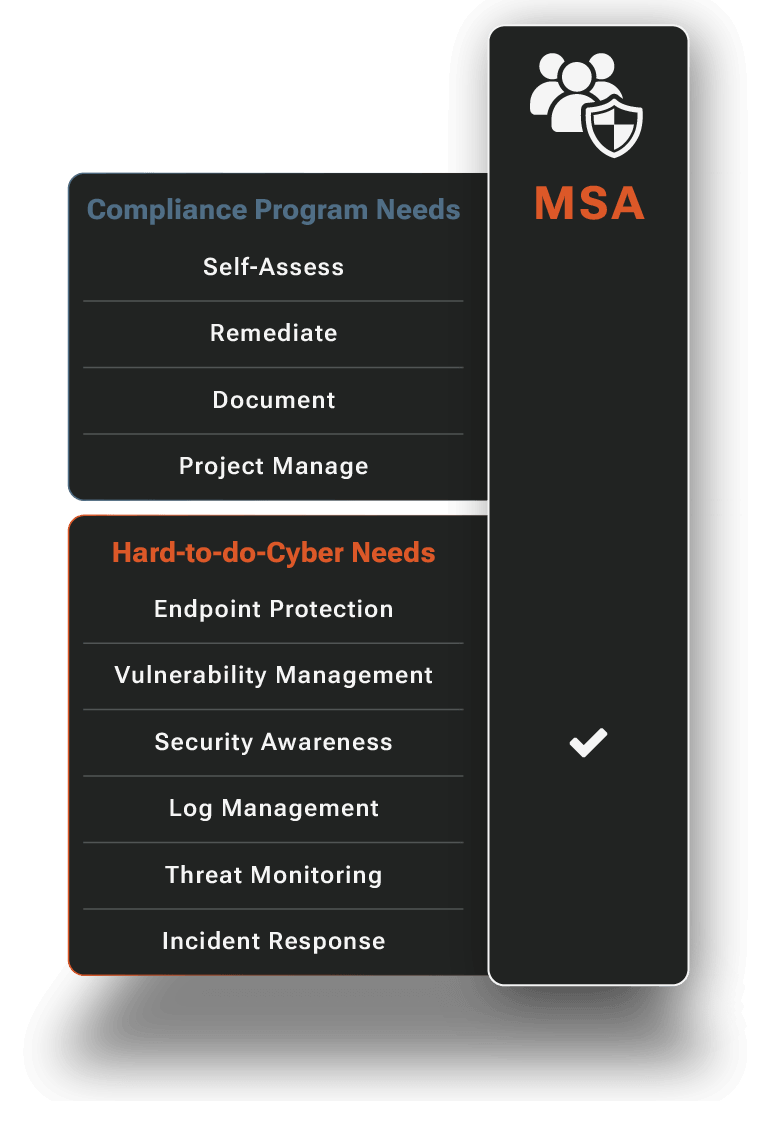
Managed Security Awareness (MSA) provides ongoing employee training and phishing simulations informed by threats observed through RADICL's vSOC. Leadership gains visibility into participation and employee risk.

  • Comprehensive Annual Training
  • Ongoing “Bite Sized” Training
  • Phishing Attack Simulations
  • Ever Evolving Expert Content
  • Security Awareness Posture Visibility
RADICL_MCA Overview
Div Line_Desktop

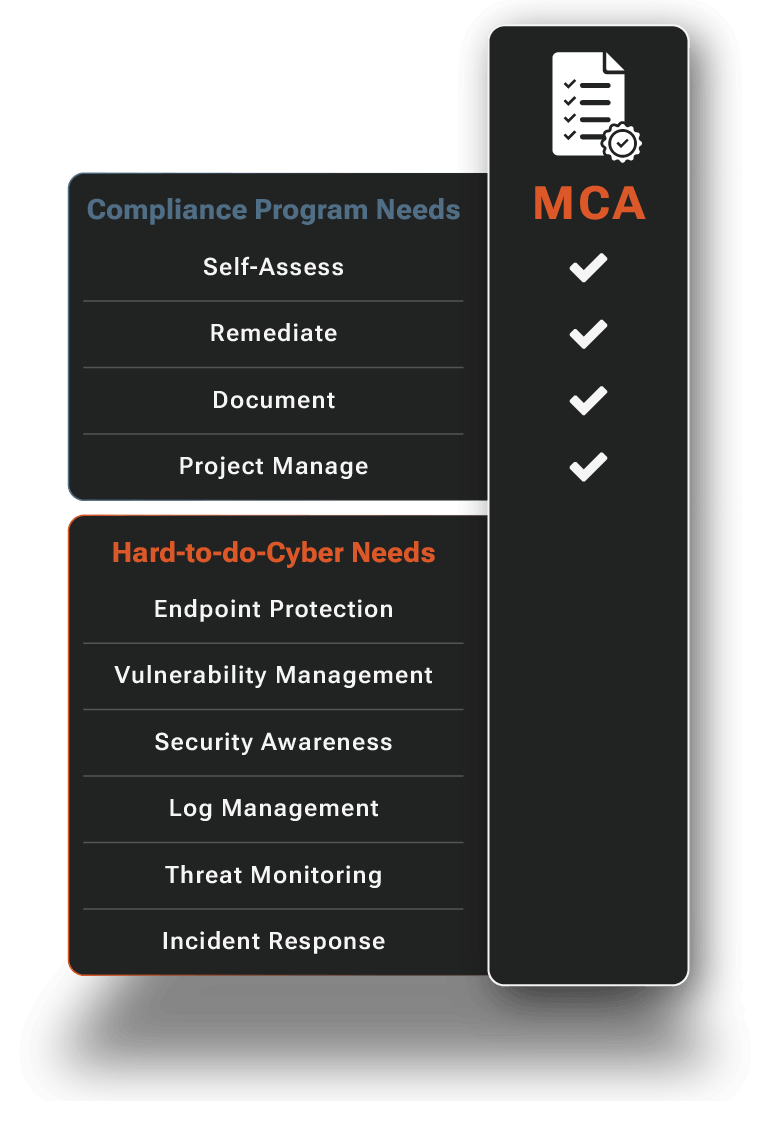
Managed Compliance Adherence for CMMC and NIST

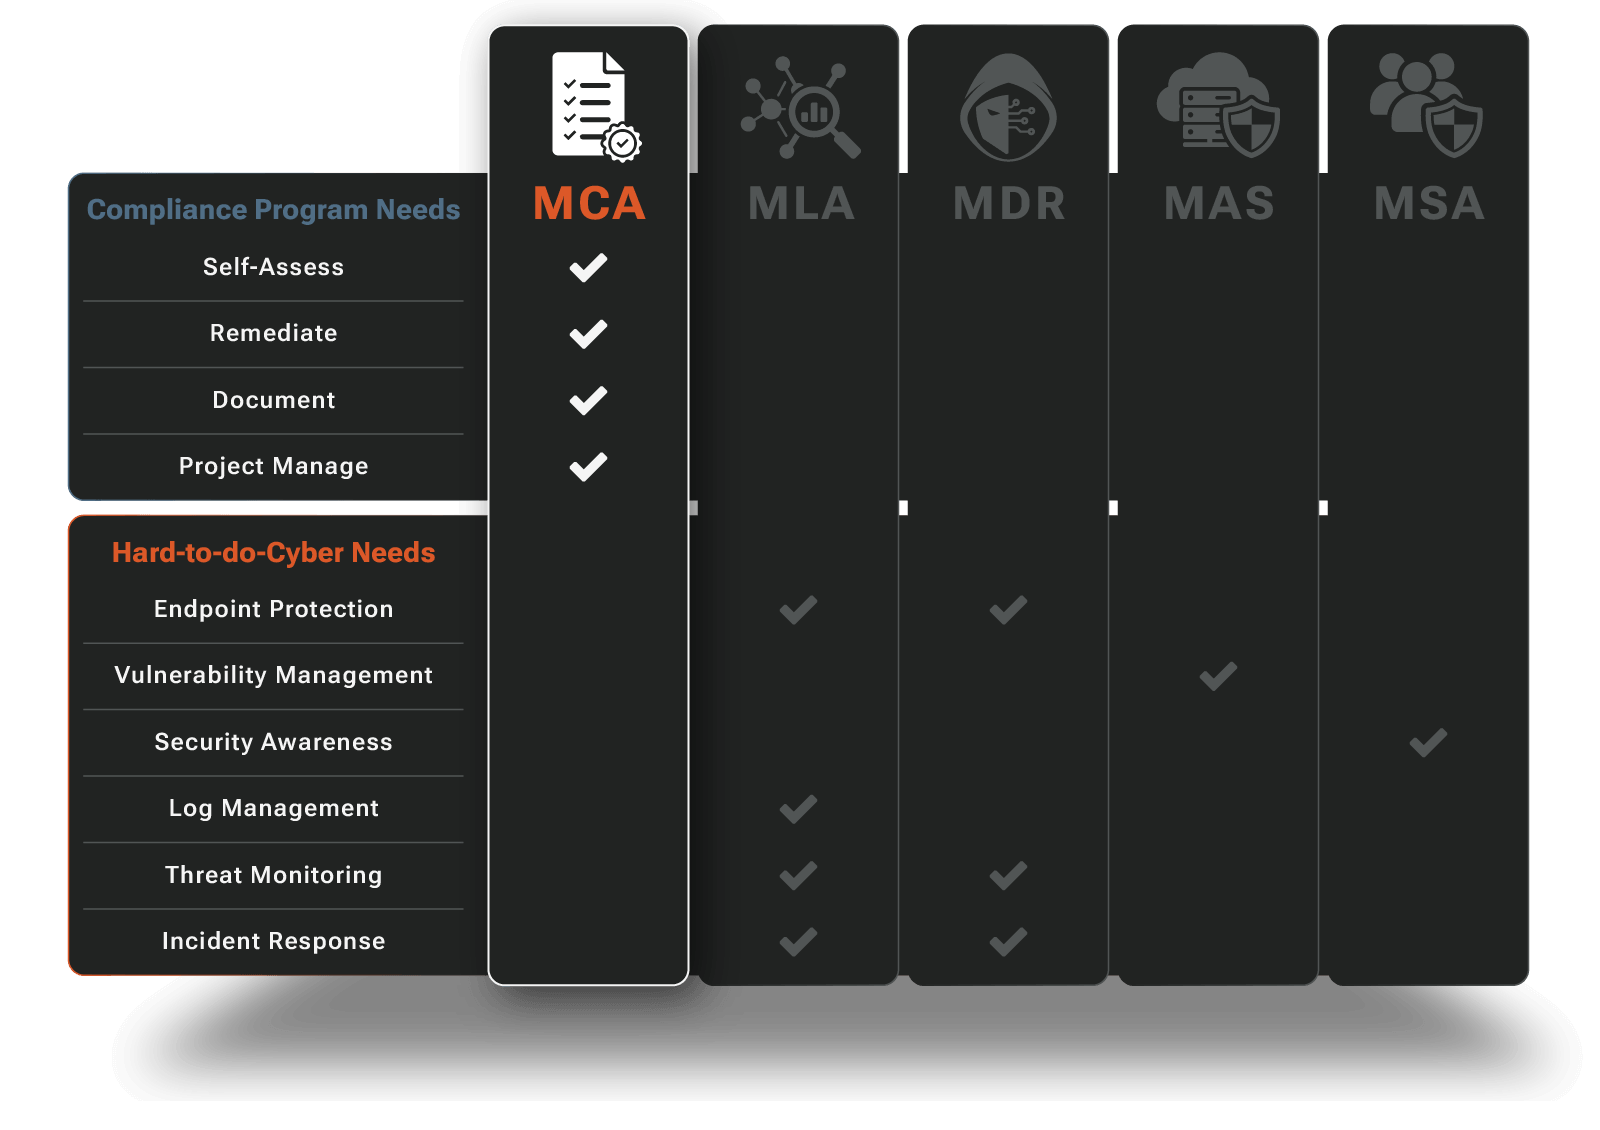
Managed Compliance Adherence (MCA) supports guided assessments, remediation guidance, documentation, evidence organization, and posture tracking for applicable NIST-based and contractual requirements.

For nuclear-sector organizations, MCA should be scoped to the requirements relevant to the engagement. It does not replace NRC licensing programs or NERC compliance functions.

RADICL provides guidance on what constitutes compliant implementation. Your organization, MSP, or other responsible partner performs required customer-side configuration and remediation.

  • Self-Assessments Guided and Made Easy
  • CMMC and NIST Adherence Gaps Quickly Closed
  • Audit Trail and Evidence Capture
  • Compliance Posture Clarity
  • External Audit Preparedness & Efficiency
RADICL_MCA Overview

RADICL's Protection Delivered Dashboard

Operational transparency gives your team visibility into the security work happening across its RADICL engagement.

The Protection Delivered Dashboard surfaces activity across investigations, incident response, vulnerability reduction, employee training, and remediation.

Our Protection Delivered Dashboard

Watch this video to learn how with RADICL, you'll enjoy real-time visibility into how we are:

RADICL Pricing

Managed cybersecurity pricing depends on your environment size, coverage scope, selected services, and required compliance support. RADICL helps you scope coverage around the systems and responsibilities your team needs supported.

View Pricing Get a Scoped Quote

Frequently Asked Questions

What is nuclear cybersecurity?

Nuclear cybersecurity protects the digital systems, networks, identities, and information used across nuclear-sector organizations. Its scope can include corporate and engineering IT, sensitive technical data, supplier environments, network boundaries, and specialized cybersecurity programs for licensed nuclear facilities.

Exact requirements differ among reactor operators, developers, engineering firms, suppliers, and other organizations.

Is nuclear cybersecurity regulated by the NRC or NERC?

Both can be relevant, but they govern different areas. The NRC regulates cybersecurity for applicable digital systems at commercial nuclear power reactors, including systems within the scope of 10 CFR 73.54. NERC CIP governs applicable Bulk Electric System cybersecurity requirements.

NRC and NERC coordinate their respective roles to avoid duplicative regulation at commercial nuclear generating facilities.

Does RADICL secure reactor or plant control systems?

RADICL should not be treated as a replacement for an NRC-regulated plant cybersecurity program or specialized OT controls protecting reactor systems.

RADICL's core managed services focus on supported endpoint, identity, network, logging, vulnerability, awareness, and security telemetry within the agreed scope.

For nuclear environments, that can include corporate and engineering IT or supported visibility around IT/OT boundaries. Plant-control responsibilities remain with the appropriate licensee, OT team, equipment vendors, and regulatory program.

What is NEI 08-09?

NEI 08-09, Cyber Security Plan for Nuclear Power Plants, is Nuclear Energy Institute implementation guidance used in nuclear power reactor cybersecurity programs.

The NRC references NEI 08-09 within its current nuclear cybersecurity materials alongside 10 CFR 73.54 and Regulatory Guide 5.71.

It is specific to the nuclear power reactor context and should not be treated as a universal cybersecurity standard for every nuclear supplier or developer.

Does RADICL make our organization NRC or NERC CIP compliant?

No provider can make an organization compliant simply by deploying a managed security service.

RADICL can operate and document defined security capabilities, organize supporting evidence, and help teams maintain security readiness within its scope.

Your organization remains responsible for determining regulatory applicability and satisfying requirements outside the RADICL engagement.

We are a nuclear supplier or new-build developer, not a plant operator — is this relevant?

Yes. Nuclear suppliers, engineering firms, and new-build developers still depend on identities, endpoints, cloud platforms, engineering systems, supplier connections, and sensitive technical information.

They may also inherit cybersecurity requirements through customers, primes, Department of Energy contracts, defense work, or other agreements.

RADICL can focus managed security on those corporate, engineering, and contract-defined environments without treating the organization as an operating reactor licensee.

Can RADICL work with our existing MSP or internal IT team?

Yes. RADICL defines responsibility boundaries during onboarding and coordinates security work with the appropriate internal team or MSP.

Your IT team or MSP can continue managing infrastructure and customer-side changes while RADICL handles the defined security operations in the engagement.

Learn more about RADICL's approach for MSPs and IT Leaders.

Do lean or growth-stage nuclear organizations need a full SOC?

No universal requirement exists for every nuclear supplier, engineering firm, or developer to build its own internal SOC.

When an organization needs continuous monitoring and response, a managed vSOC can provide 24/7 coverage without staffing the entire function internally.

The appropriate model still depends on your role, systems, contracts, and regulatory responsibilities.

What proof do we get for regulators, primes, and partners?

Available records depend on the RADICL services in scope.

They can include security cases, investigation records, retained logs, vulnerability-remediation history, awareness records, exercises, tasks, and supporting files.

RADICL keeps those records connected to the security work that produced them. The regulator, customer, prime, or other reviewing authority determines what evidence is required for a specific review.

How fast can we get monitoring and evidence workflows in place?

RADICL's standard vSOC deployment can be operational in 7 days for supported environments, with endpoints protected and 24/7 response ready.

Broader integrations, evidence workflows, compliance baselining, and customer-specific requirements can take longer depending on your environment, scope, and access.

For nuclear organizations, deployment planning must also follow any applicable plant, OT, contractual, or regulatory constraints.